

Create a Replication Workflow
Prerequisites
Create a source bucket with versioning enabled.
Create one or multiple cloud storage locations with versioning enabled to use as targets for replication.
Create one or multiple Cross-Region Replication Locations.
Procedure
Important
Only one replication rule can be created per source bucket.
From the main menu, choose Data Management. Click Data Browser from the side menu and select an account from the top drop-down list in the breadcrumb.

Select the bucket you want to view by clicking anywhere on the row but the bucket name.
In the Replication tab, click Create Rule.
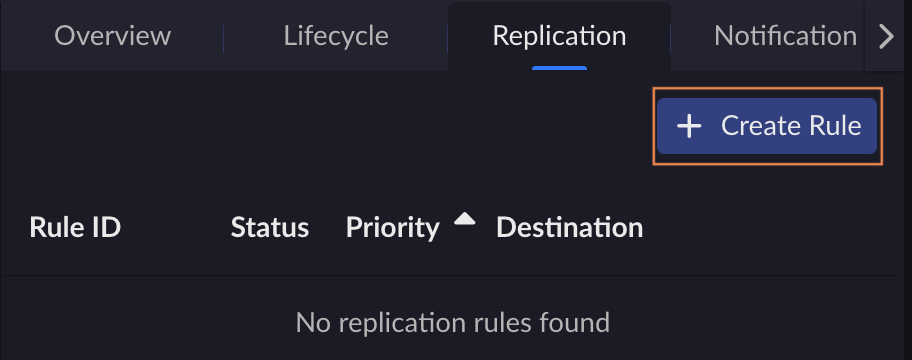
The Create Replication Rule page opens with a form to fill in the rule details and the replication actions to enable.
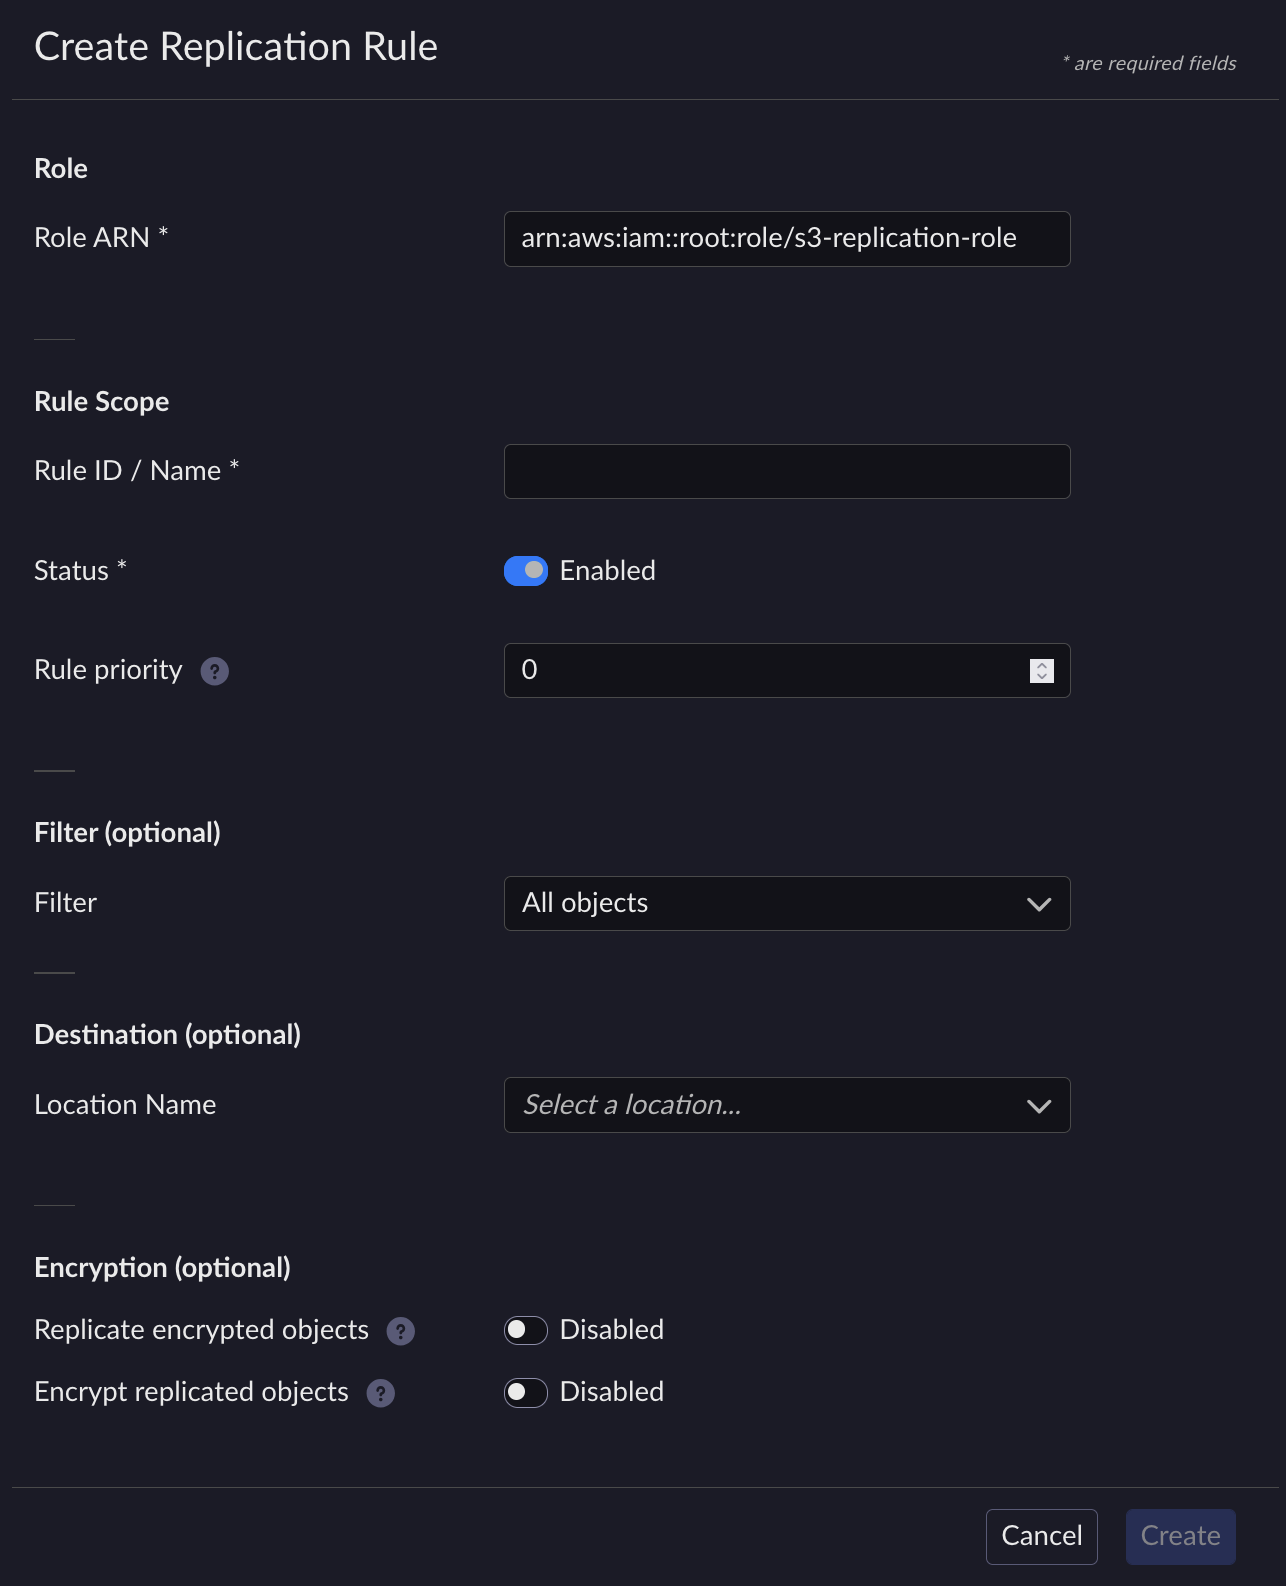
Fill in the required fields:
Role ARN: Select the IAM role(s) to use for replication.
Standard Location
Use the default IAM replication role
arn:aws:iam::root:role/s3-replication-role.Cross-Region Replication Location
Specify the IAM source role
arn:aws:iam::root:role/s3-replication-roleand the IAM destination role previously created.The two roles must be specified in a comma-separated list, for example:
arn:aws:iam::root:role/s3-replication-role,arn:aws:iam::<account-id>:role/<role-name>.Rule ID / Name: Enter a unique identifier for the rule.
Status: Select Enabled or Disabled.
(Optional) Configure Filters to limit replication scope:
Prefix: Apply the rule only to objects matching a key prefix.
Tags: Apply the rule only to objects with specific tag key-value pairs.
(Optional) Configure a Destination to specify the storage location for replicated objects.
Location Name: Select the destination storage location.
Note
For a Cross-Region Replication (CRR) location, additional fields are displayed such as the Target Bucket Name. This field is used to specify the destination bucket name in the replication configuration.
Click Create.
The new rule displays under the bucket’s Replication tab.
Configure the JSON object with the following syntax.
{
   "Role": "arn:aws:iam::root:role/s3-replication-role",
   "Rules": [
      {
         "Status": "Enabled",
         "Prefix": "",
         "Destination": {
            "Bucket": "arn:aws:s3:::destination-bucket",
            "StorageClass": "target-storage-location"
         }
      }
   ]
}
In the
Rolefield, specify the IAM source role.In the
Prefixfield, specify a prefix filter to apply the replication rule only to objects belonging to a certain prefix.In the
Destinationfield, specify the destination bucket and a unique, or a comma-separated list of destination Data Storage locations.
Use the following PUT Bucket Replication S3 command.
aws --endpoint-url http://endpoint s3api put-bucket-replication --bucket source-bucket --replication-configuration file://replication.json
Configure the JSON object with the following syntax.
{
   "Role": "arn:aws:iam::root:role/s3-replication-role,arn:aws:iam::746805127671:role/everything-by-everyone",
   "Rules": [
      {
         "Status": "Enabled",
         "Prefix": "",
         "Destination": {
            "Bucket": "arn:aws:s3:::destination-bucket",
            "StorageClass": "target-storage-location"
         }
      }
   ]
}
In the
Rolefield, specify the IAM source rolearn:aws:iam::root:role/s3-replication-roleand the IAM destination role previously created.In the
Prefixfield, specify a prefix filter to apply the replication rule only to objects belonging to a certain prefix.In the
Destinationfield, specify the destination bucket and the CRR location previously created.
Use the following PUT Bucket Replication S3 command.
aws --endpoint-url http://endpoint s3api put-bucket-replication --bucket source-bucket --replication-configuration file://replication.json
Note
Refer to Replication Monitoring for more information on dashboards.


