

Configure Bucket Policy
Bucket policies are resource-based policies that grant access permissions to buckets and the objects in them. Use bucket policies to manage access for IAM users, roles, and other AWS accounts without modifying individual user permissions.
Prerequisites
A bucket exists (refer to Create a Bucket).
A user with the StorageManager role is available (refer to Create a Local User).
Tip
For more information on S3 bucket policies, refer to Using bucket policies.
Procedure
From the main menu, choose Data Management. Click Data Browser from the side menu and select an account from the top drop-down list in the breadcrumb.

Select the bucket you want to view by clicking anywhere on the row but the bucket name.
In the bucket Overview tab, locate the Permissions section. The Bucket Policy field indicates whether a policy is configured (Configured or Not configured).
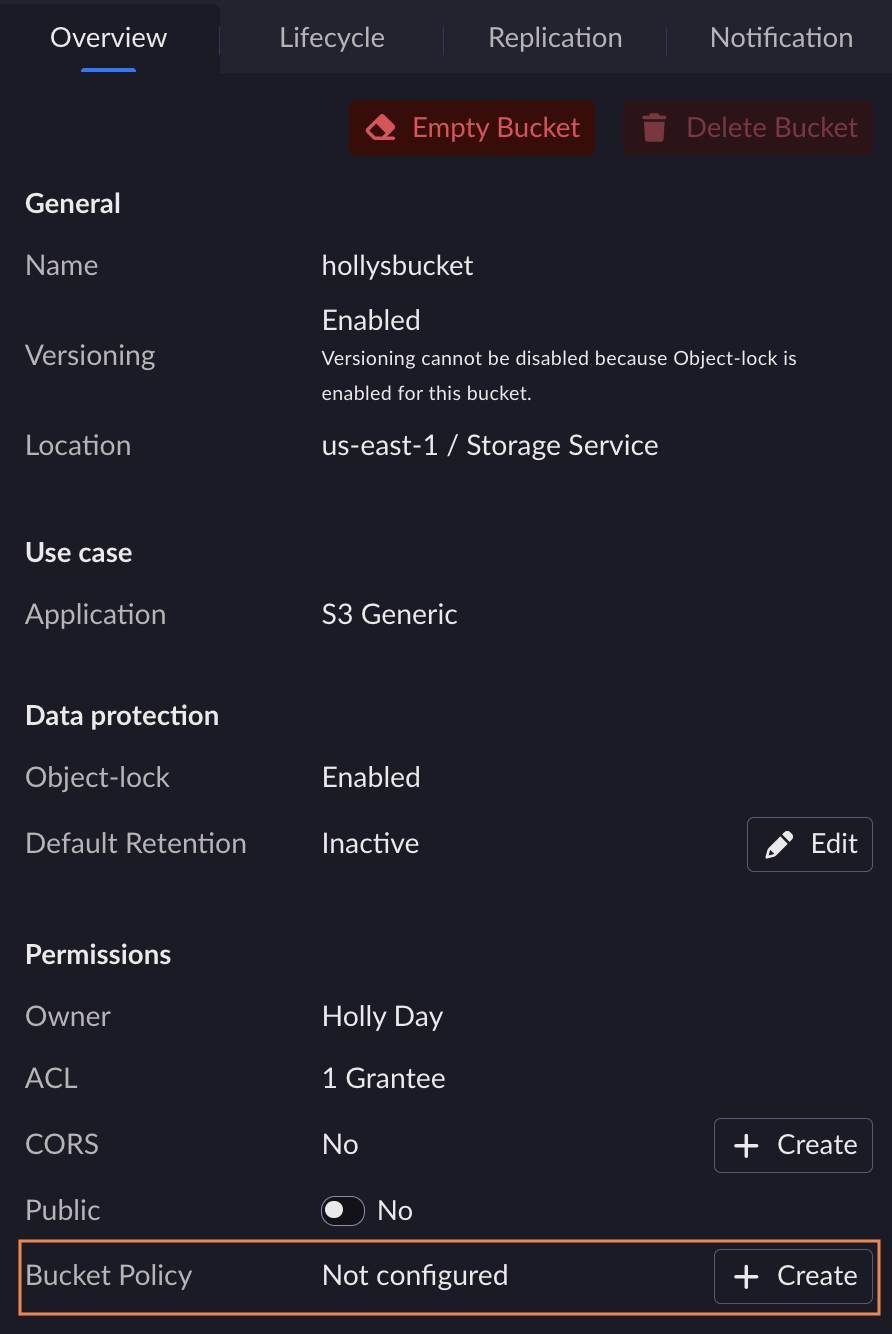
Click the Create or Edit button next to the Bucket Policy field.
The Create Bucket Policy or Edit Bucket Policy page opens with a JSON editor that supports schema validation.
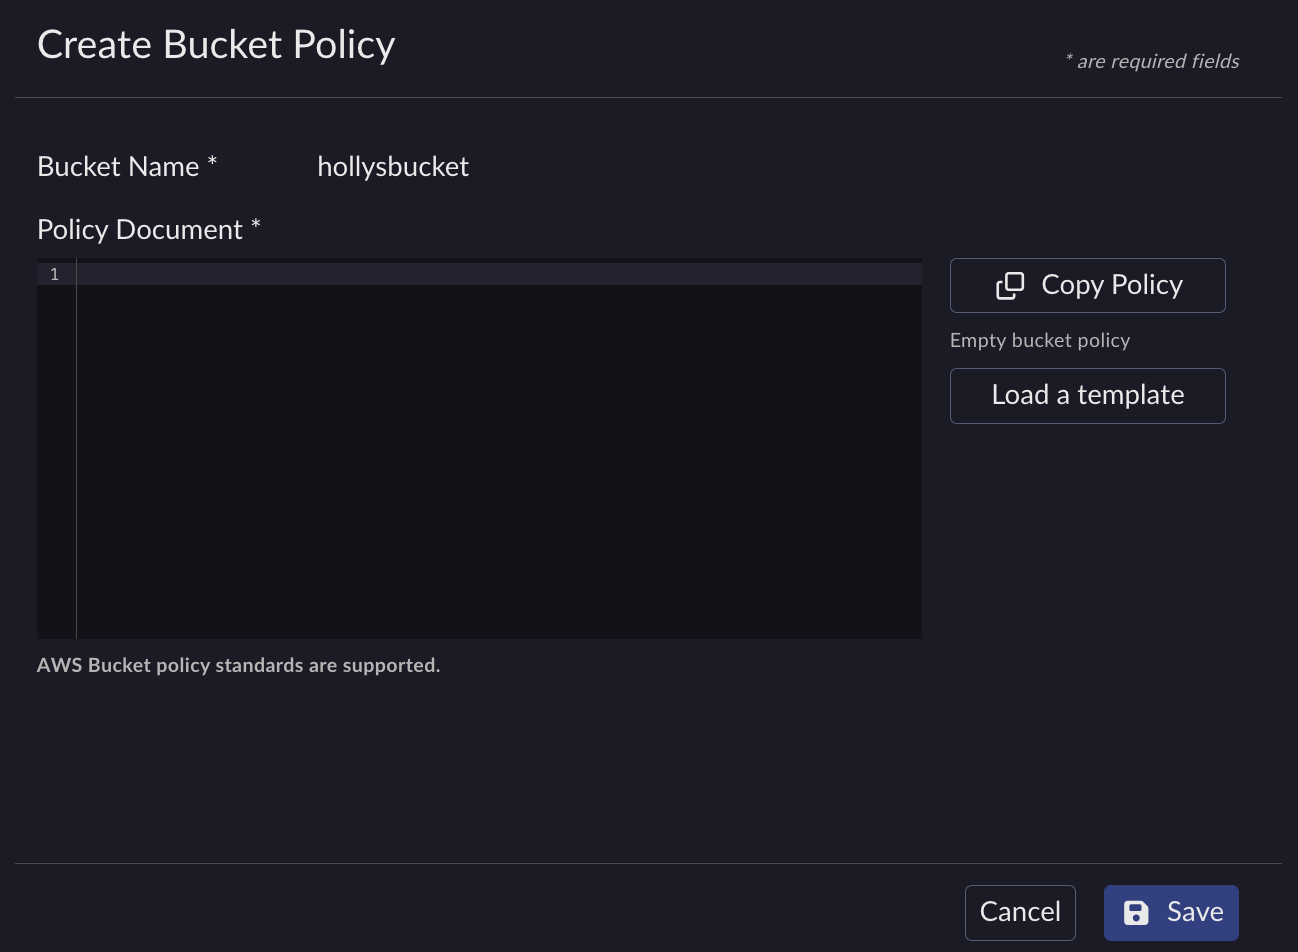
Enter the bucket policy in JSON format. The policy follows the standard IAM policy structure with the following elements:
Version: Policy language version (use
"2012-10-17").Statement: Array of permission statements, each containing:
Sid: Optional statement identifier.
Effect:
"Allow"or"Deny".Principal: The account, user, role, or service to grant or deny access.
Action: The S3 actions to allow or deny (for example,
"s3:GetObject").Resource: The bucket or object ARN the statement applies to.
Condition (optional): Conditions under which the policy is in effect.
Tip
Click Load a template to populate the editor with a sample bucket policy.
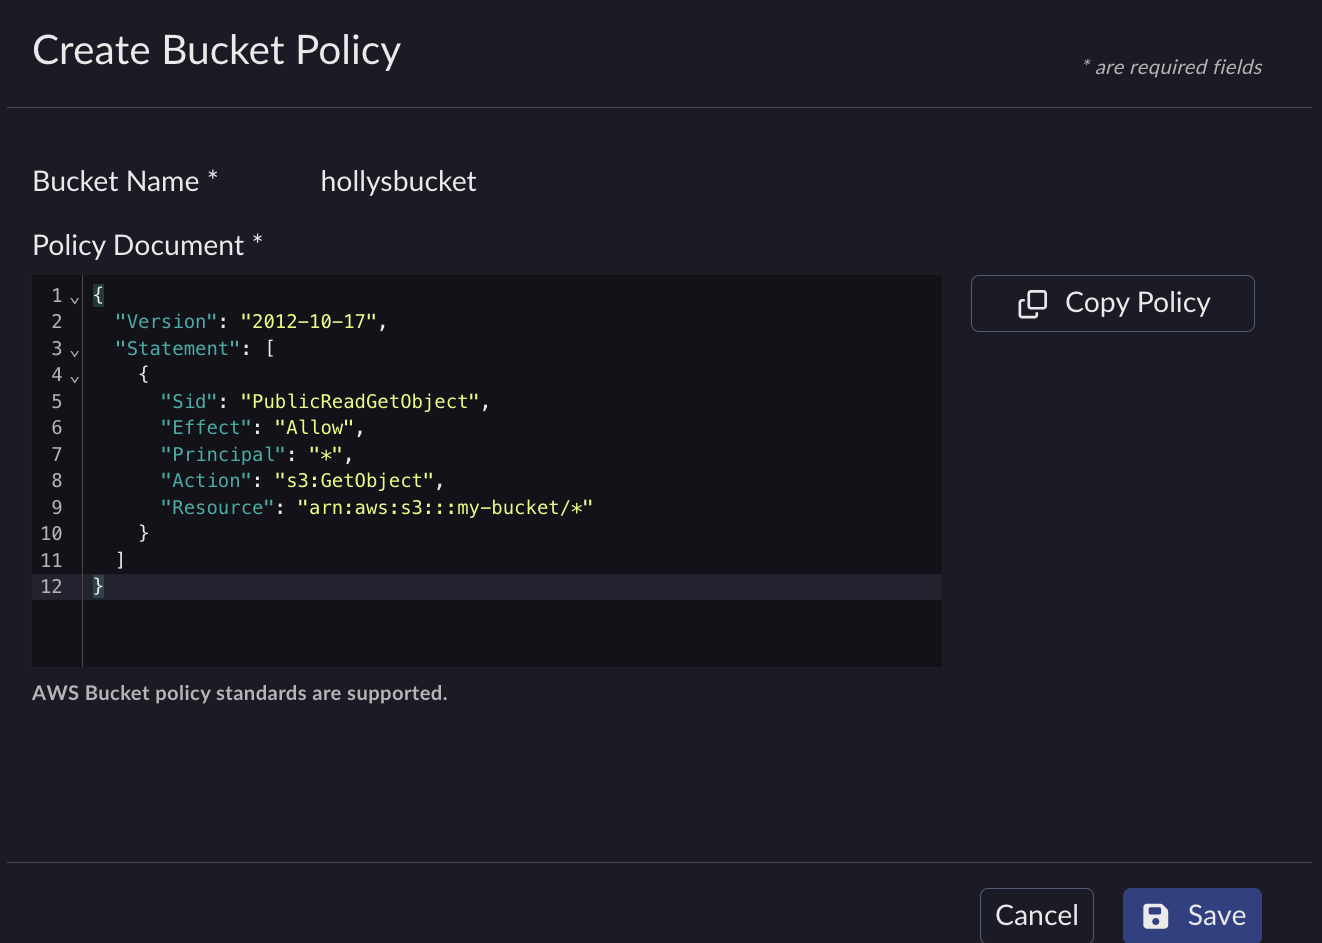
Example of a bucket policy
{
  "Version": "2012-10-17",
  "Statement": [
    {
      "Sid": "PublicReadGetObject",
      "Effect": "Allow",
      "Principal": "*",
      "Action": "s3:GetObject",
      "Resource": "arn:aws:s3:::my-bucket/*"
    }
  ]
}
Click Save to apply the bucket policy.
To remove the bucket policy, clear the editor content and click Save.
To configure a bucket policy:
aws --endpoint-url http://endpoint s3api put-bucket-policy --bucket BUCKET_NAME --policy file://policy.json
To retrieve a bucket policy:
aws --endpoint-url http://endpoint s3api get-bucket-policy --bucket BUCKET_NAME
To delete a bucket policy:
aws --endpoint-url http://endpoint s3api delete-bucket-policy --bucket BUCKET_NAME


