

Manage Truststore
The truststore allows ARTESCA, acting as a TLS client, to check the authenticity of remote servers. It stores CA certificates used to validate the certificate chain presented by a server during a TLS handshake. If the server’s certificate chain is signed by a trusted CA contained in the truststore, the TLS connection is accepted. If it is not signed by a trusted CA, it is rejected.
The Truststore feature is used when configuring a remote location whose endpoint presents a non-public or privately signed TLS certificate. It is also required when setting up a replicated location. The truststore allows ARTESCA to validate the server’s certificate and establish a trusted TLS connection.
Imported CA certificates have an expiration date. Upon expiration, it is impossible to renew a certificate. It is necessary to delete the expired certificate and import a new one.
Warning
If needed, external locations can be accessed while skipping the TLS verification on certificates. Scality does not recommend enabling this option as the ARTESCA platform will be unable to verify the external location’s identity as well as its ability to repudiate it. Data remain encrypted but the secure channel verification will be bypassed.
Skip/Activate TLS Verification
In the Data Management menu, access the Truststore page.
Check the TLS Verification status at the top right of the page.
If Active is displayed, TLS verification is enabled.
If Skipped is displayed, TLS verification is disabled.
Click the pen icon under TLS Verification to edit the setting.
Based on your TLS verification status, a modal will be displayed:
If TLS Verification is set to Active, a modal will be displayed to confirm that you want to skip the TLS verification.
If TLS Verification is set to Skipped, a modal will be displayed to confirm that you want to activate the TLS verification.
Important
Switching the TLS verification from one status to another will take some time.
To prevent service interruption when activating the TLS verification, ensure that you import the certificates of the external locations.Click the confirmation button stating that you understand the impact of this action.
Click Confirm.
To set up a secured communication using the Truststore feature, follow this workflow:
Retrieve the Remote Server’s CA Certificate
This procedure allows you to retrieve the CA certificate needed to establish a secured connection from an ARTESCA deployment to a remote server.
Note
This procedure is documented for a remote ARTESCA server, but it could be another kind of server if needed.
Click the username in the top right-hand corner of the ARTESCA UI and select Certificates from the drop-down list.
Note
The username in the following image is Holly Day.
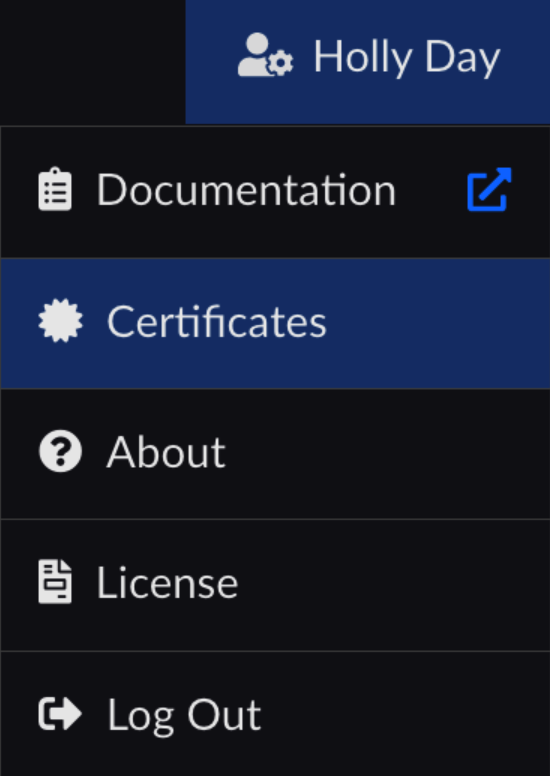
The list of certificates is displayed.
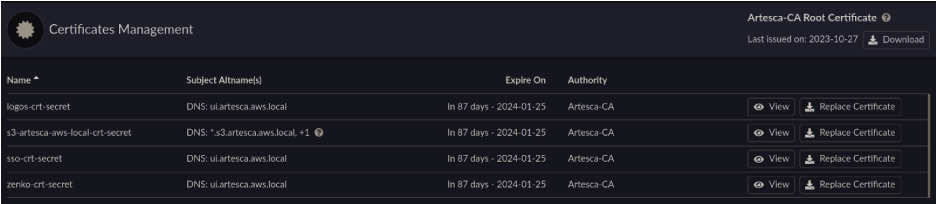
Click Download on the top right under Artesca-CA Root Certificate.
Import the Retrieved CA Certificate in the ARTESCA Deployment
This procedure allows you to import the CA certificate retrieved in the ARTESCA truststore.
Note
The Truststore page is only available when accessing the UI using https://<Mngt IP>:8443. Otherwise, the Truststore entry menu will not be displayed in the DataManagement menu.
Click Data Management on the top menu.

Click Truststore in the left banner.
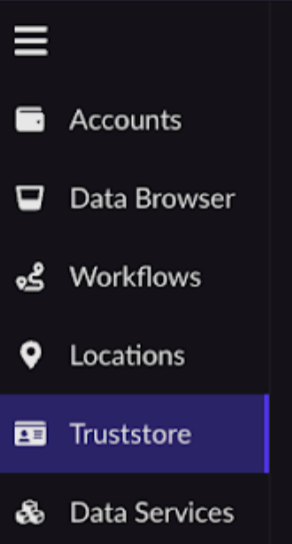
Click Import Certificate.
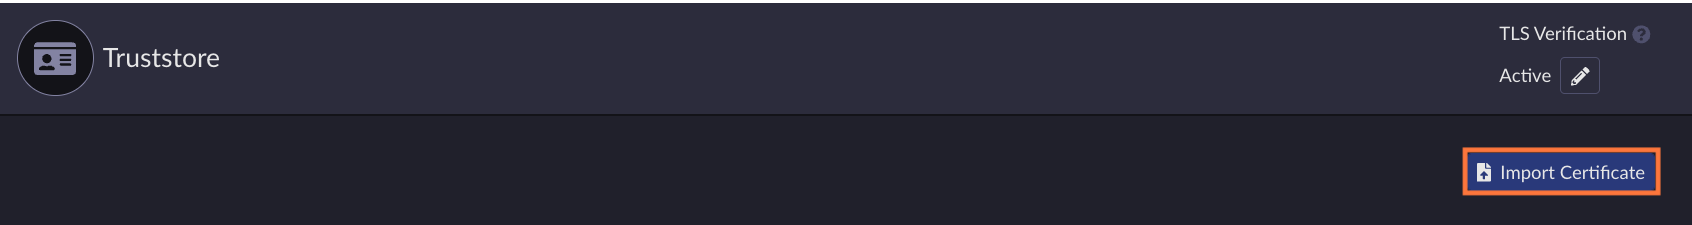
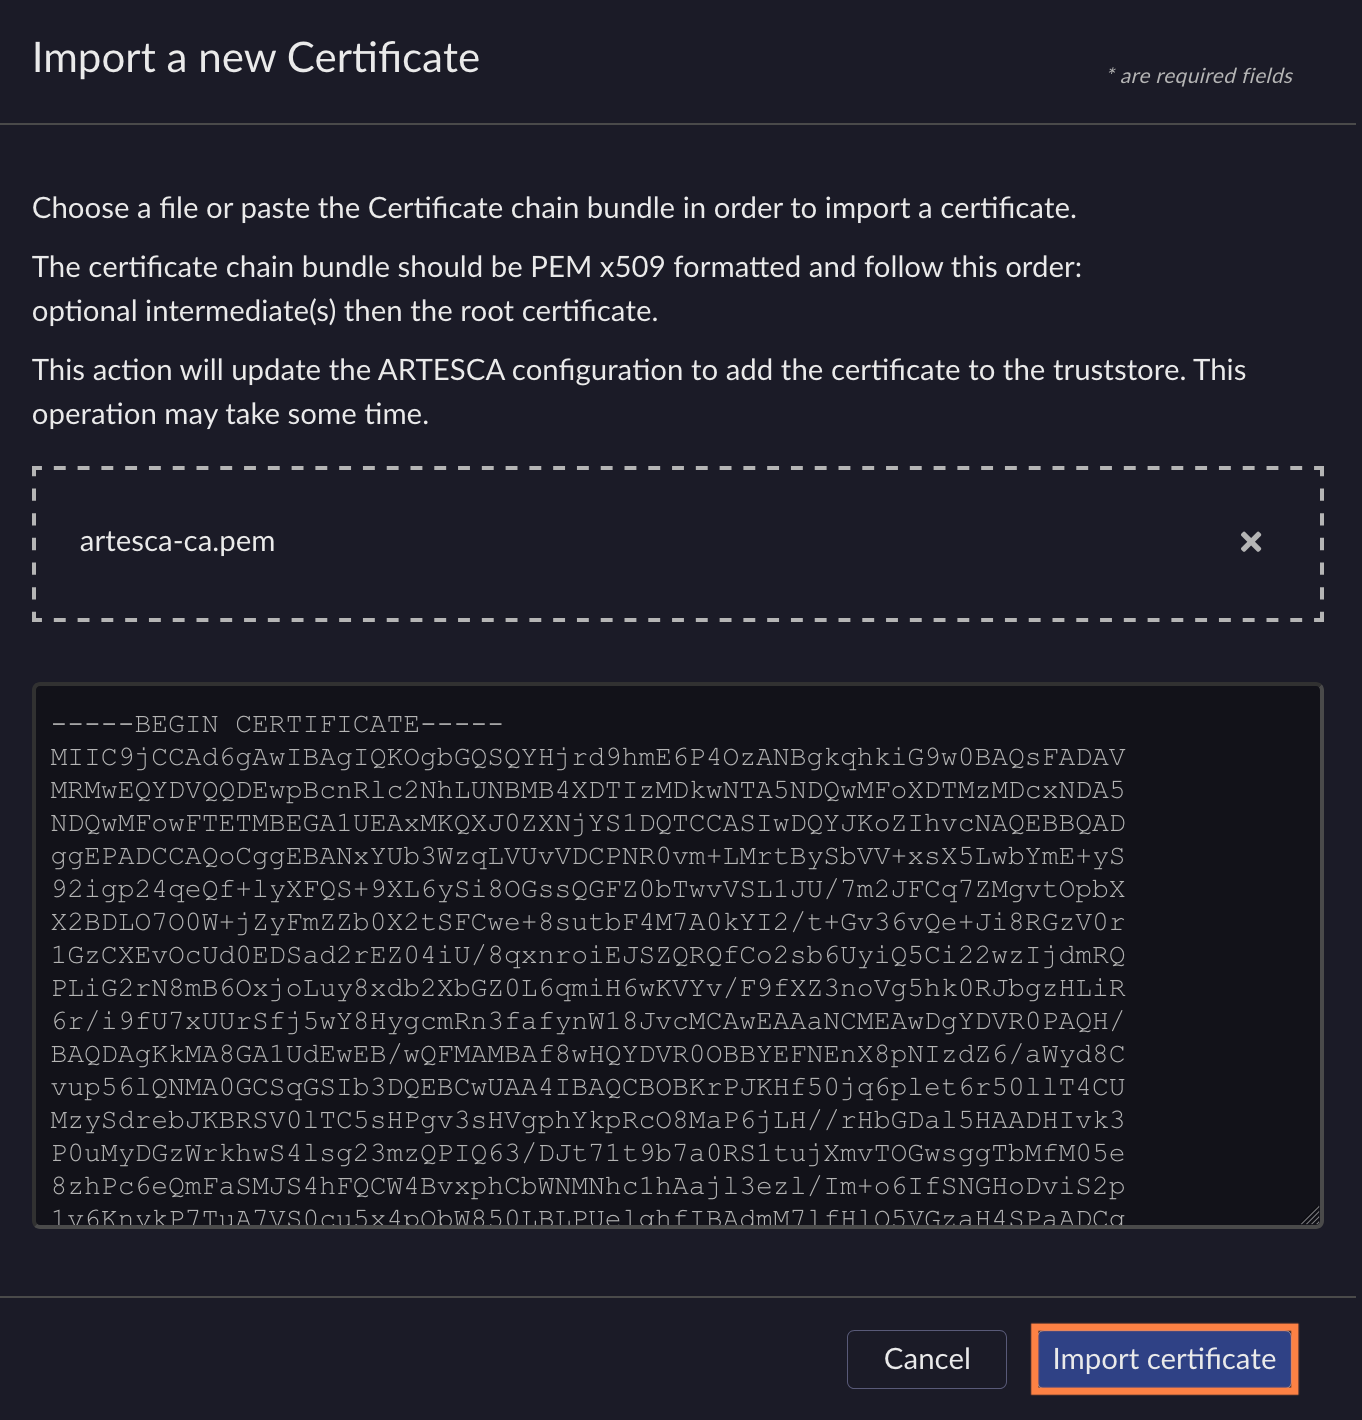
Import the previously retrieved CA certificate —by browsing, drag-and-dropping or pasting the certificate— and click Import certificate.
The newly imported CA certificate is displayed in the Truststore table.
Tip
Click View Details to access detailed information about the CA certificate and to download it.
Understanding CA Certificate Naming
For CA certificates that were imported with optional intermediate(s) and the root certificate, the name is:
intermediate > root.For CA certificates that were imported only with the root certificate, the name is:
root.


