Veeam Kasten
Veeam Kasten is a Kubernetes-native backup solution that enables backup and restoration of Kubernetes applications and their volumes. Veeam Kasten is particularly beneficial in disaster recovery and application migration scenarios, as it automatically discovers the applications installed within the relevant Kubernetes cluster.
To allow storing of snapshots external to the Kubernetes cluster, Veeam Kasten supports S3-compatible storage as an external storage using the concept of Location Profiles.
Prerequisites
Veeam Kasten
ARTESCA is installed using
kasten --partner-application
Storage Profile
Veeam Kasten uploads objects to ARTESCA’s bucket with an average object size of 20 MB.
Performance
The following performances were observed on standard configuration with flash drives and 25Gbps network:
Architecture |
Backup |
Restore |
|---|---|---|
1 node |
Up to 5.5 TB/H |
4 TB/H |
3 nodes |
Up to 8 TB/H |
6 TB/H |
6 nodes |
Up to 12 TB/H |
9 TB/H |
Best Practices
The following parameters can be adjusted to control Kasten’s performance that may be tuned according to the needs of the environment.
services.executor.workerCount
executorReplicas
limiter.csiSnapshots
limiter.providerSnapshots
For more information on Kasten performance tuning, refer to Veeam Kasten for Kubernetes Performance documentation.
Configure ARTESCA for Kasten
Access the connector page:
On first login, as no account exists, the connector page displays.
Click Start ISV Connector.
From the Accounts page.

From the Data Browser page.

Note
This option is only available if you have already created an account.
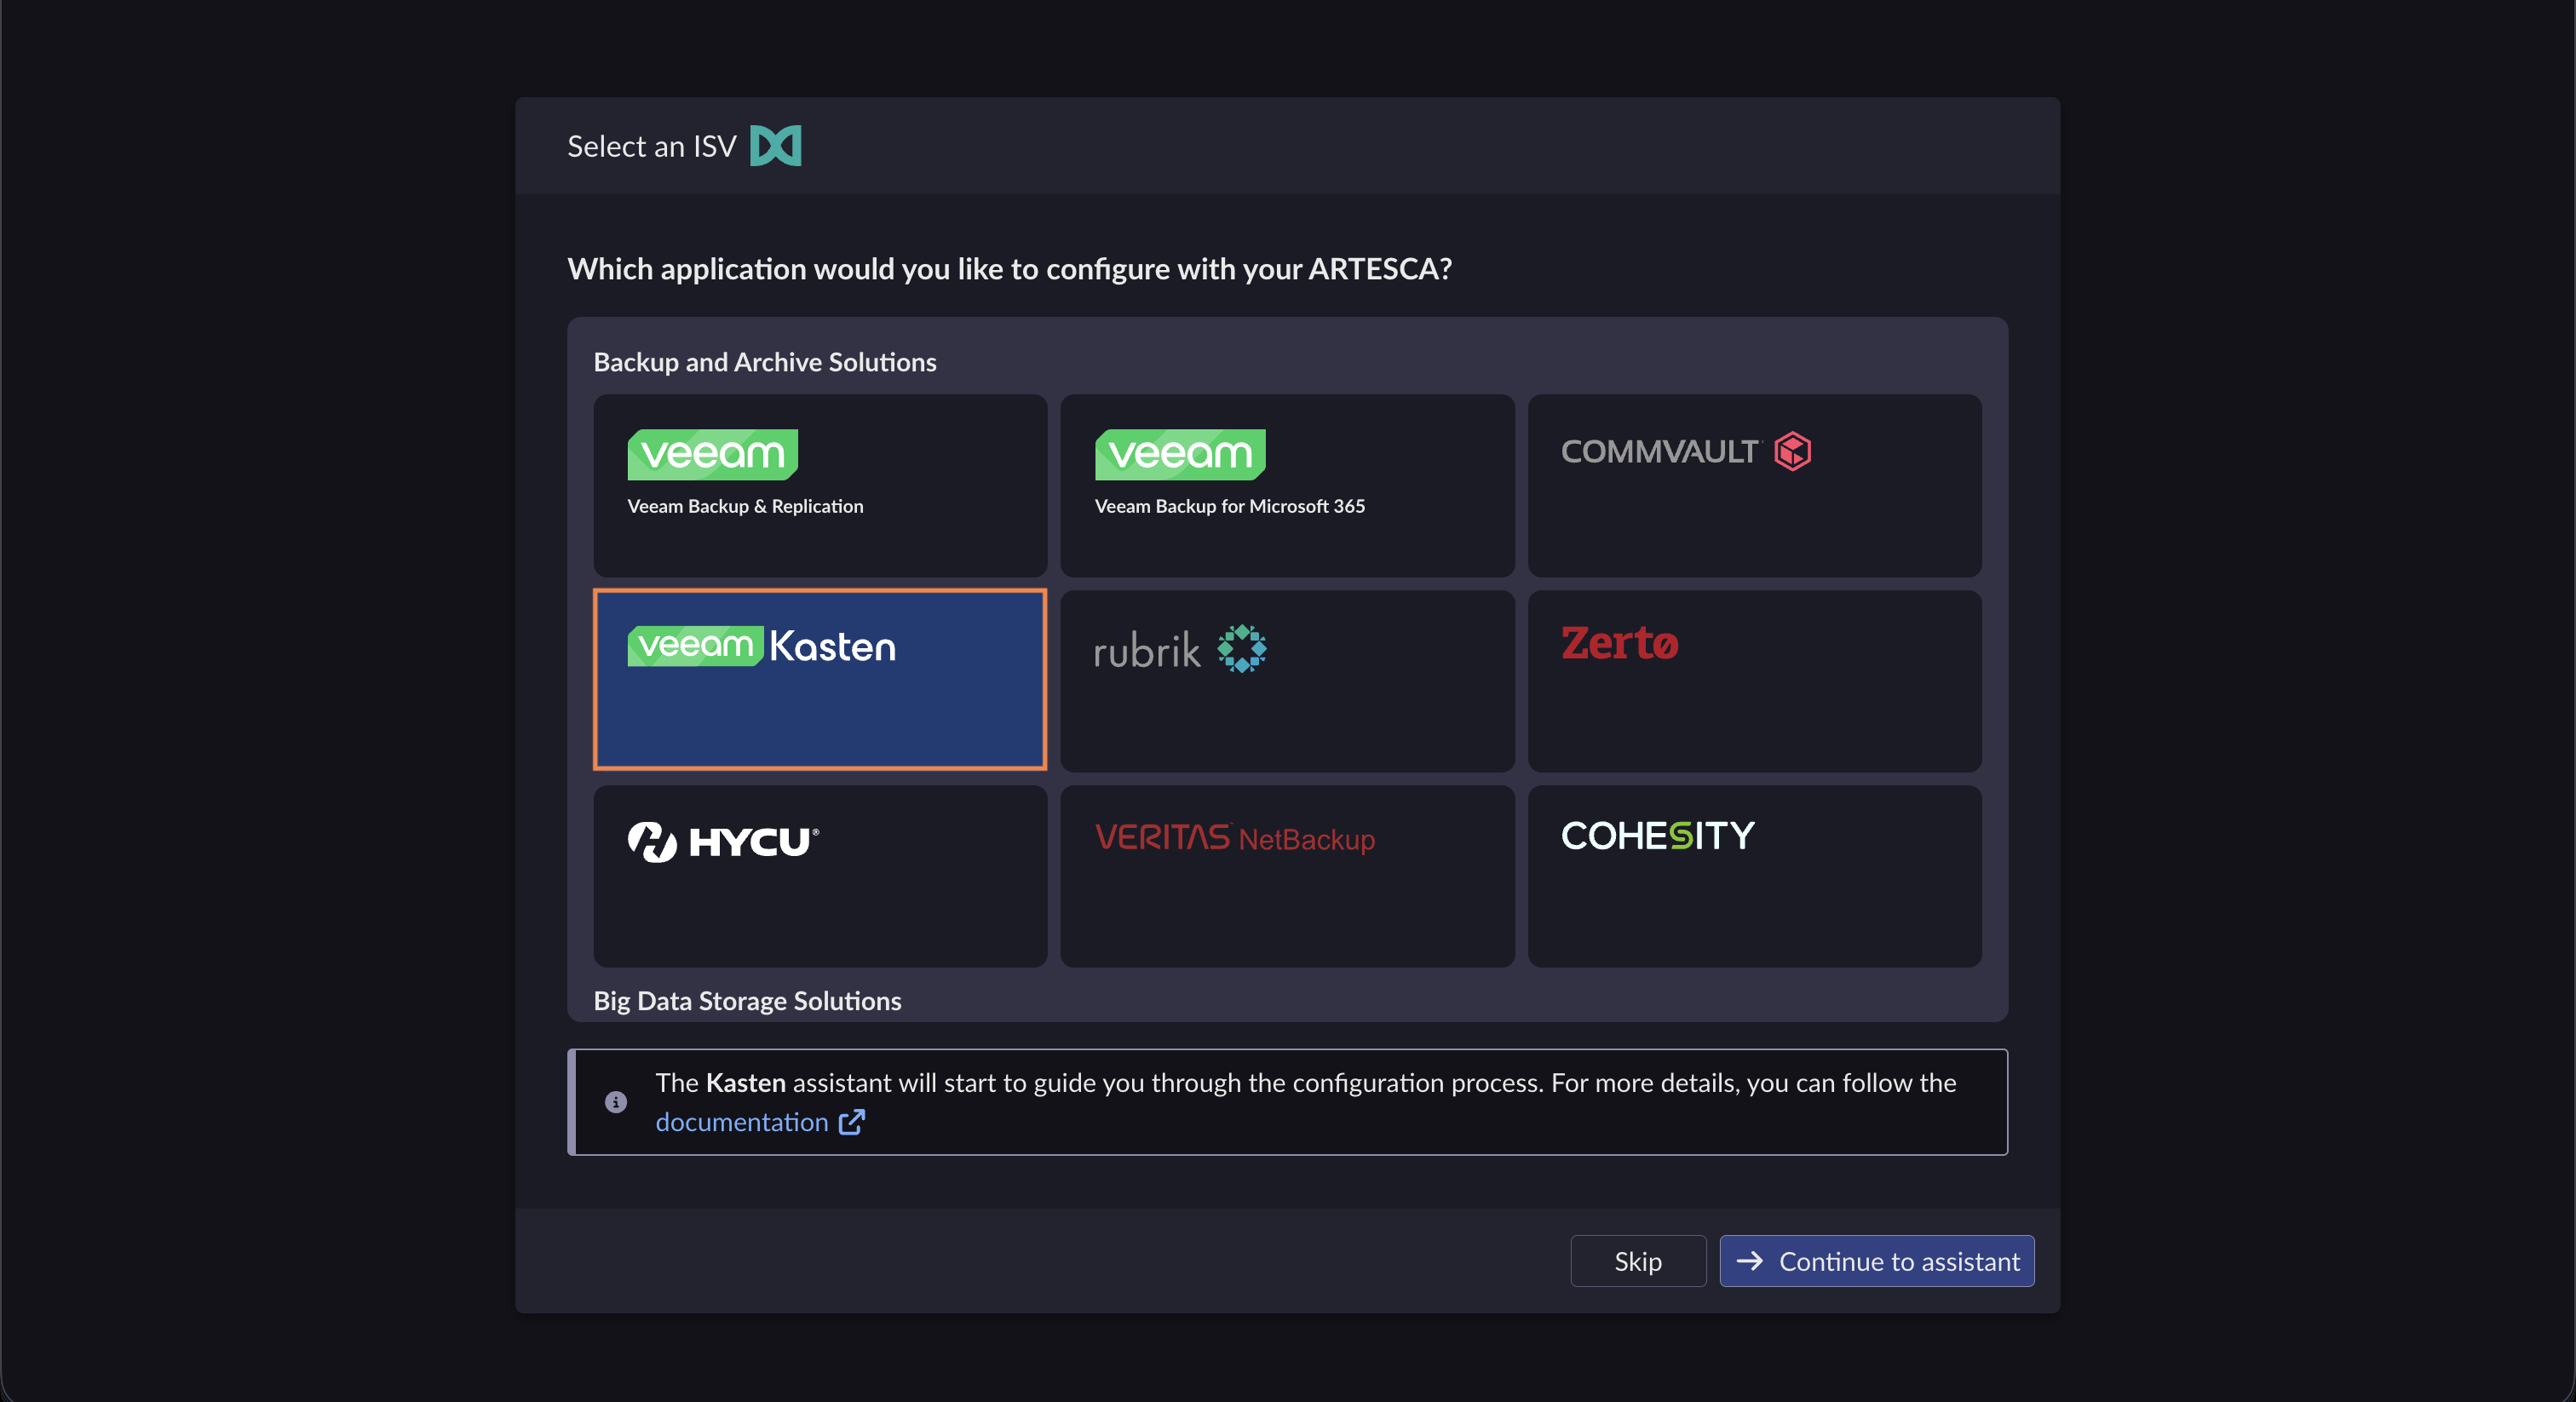
On the connector page, select the Veeam Kasten partner application, and click Continue to assistant.
Fill in the required fields.
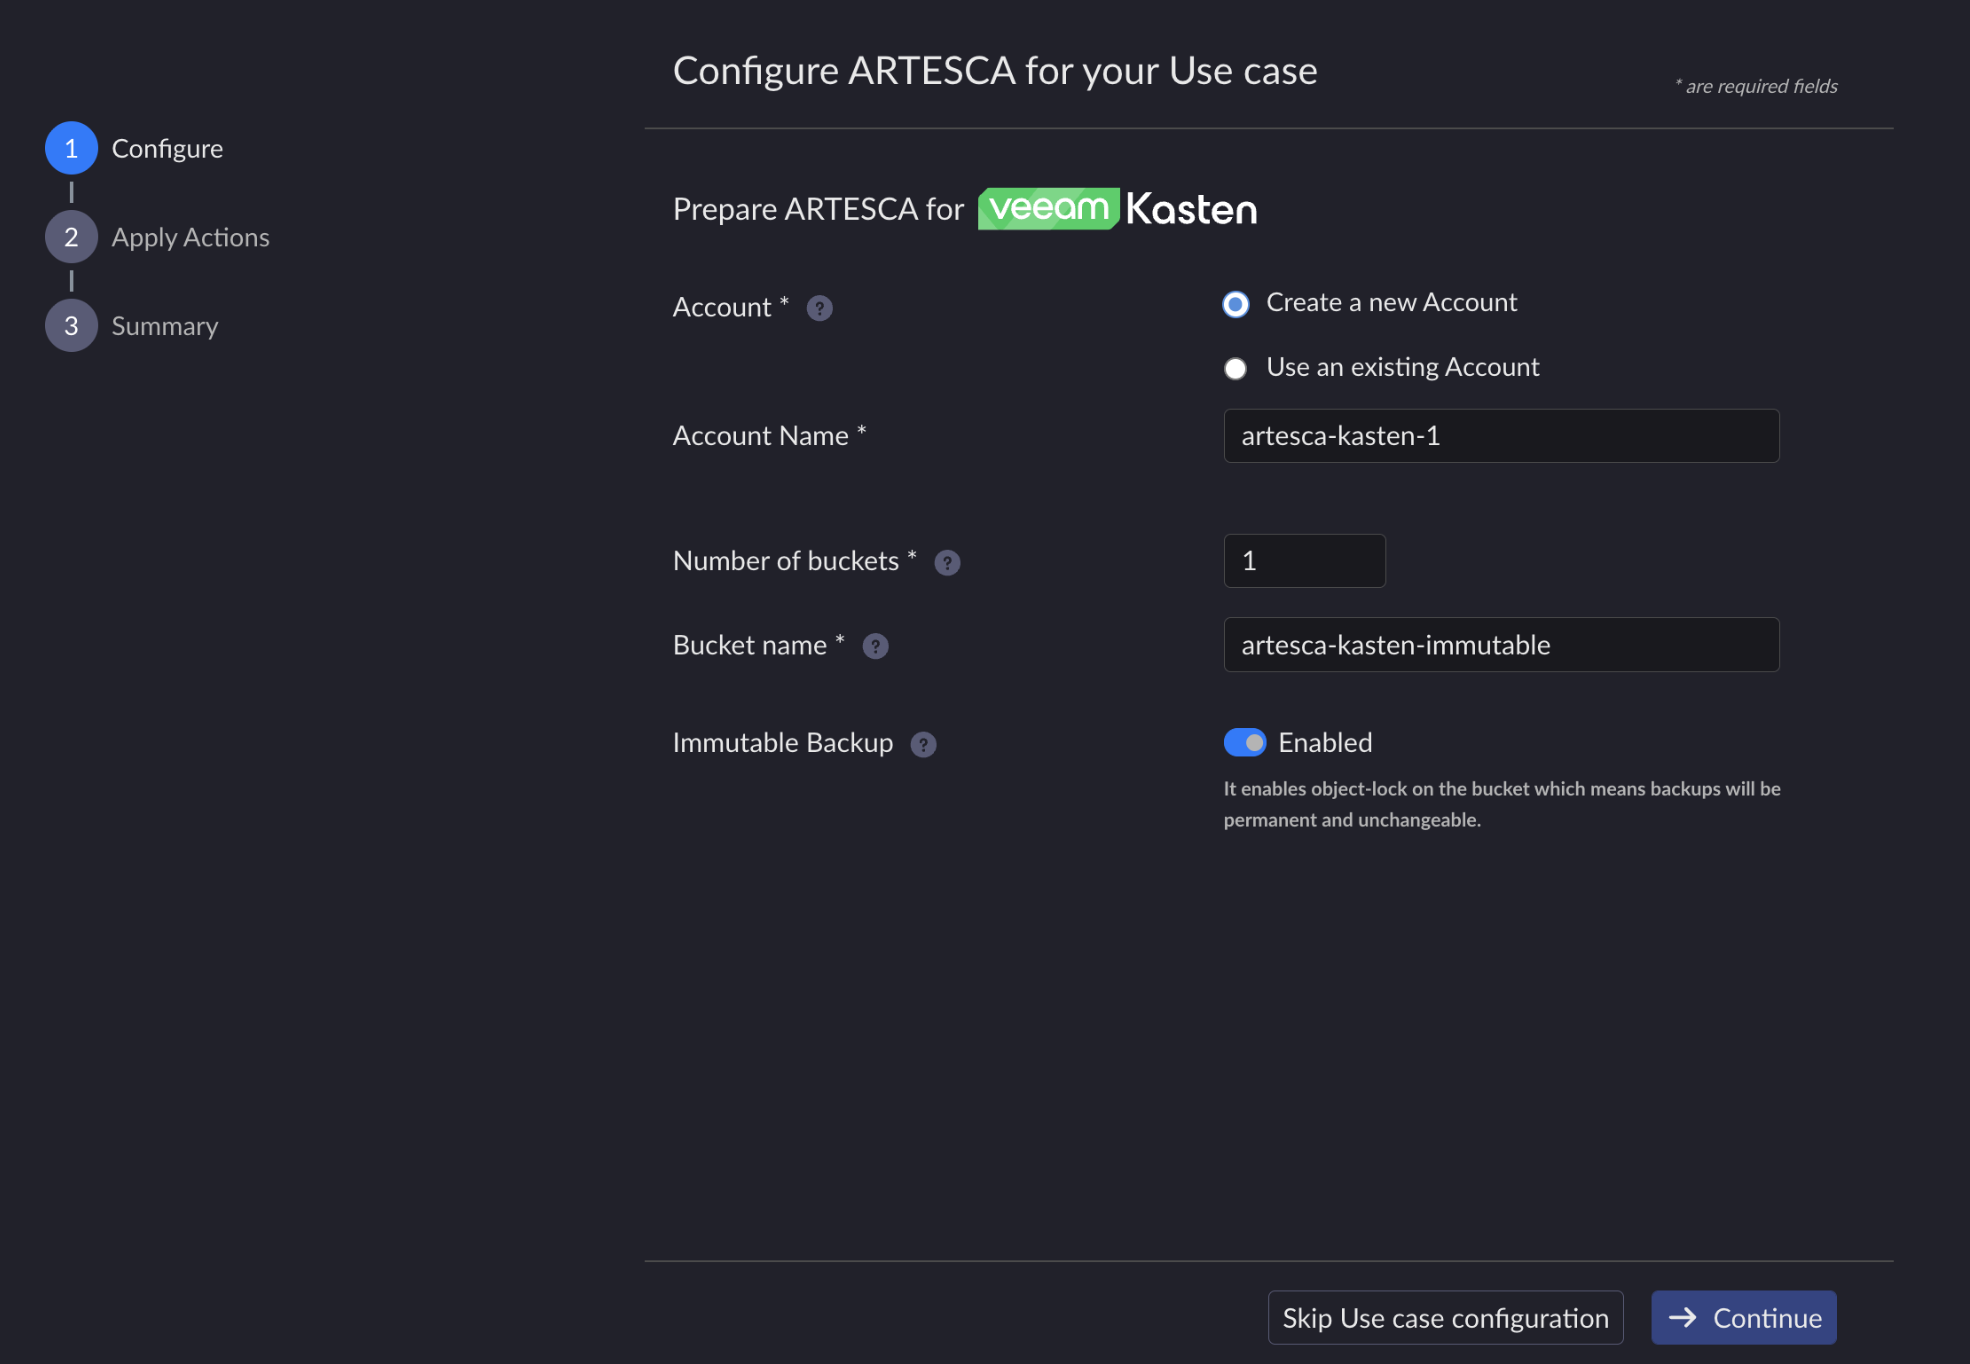
Field Descriptions
Field
Description
Account
Create a new account: Select this option if you want to create a new account.
Use an existing account: Select this option if you want to use an existing account. This option is only available if you have already created an account.
Note
If starting the configuration from the Data Browser page, this field is automatically pre-filled and locked.
Account Name
Enter the name of the account you want to create or choose an already existing account from the drop-down list.
Advanced settings
This field is only available if selecting the Use an existing account option.
By default, the system checks if an IAM user already exists for the given account and partner application. If a matching user is found, the system will preselect it and extend its permissions without creating new AK/SK credentials.
Create a new IAM user: Select this option if you want to create a new IAM user within your existing account. In that case, you must provide an IAM user name.
Use an existing IAM User: Select this option if you want to use an existing IAM user. In that case, choose the user from the drop-down list. You can also choose to generate a new set of AK/SK credentials.
Number of buckets
Choose the number of buckets you want to create. The limit is 20 buckets.
Bucket name
Enter a unique name for the bucket. The name must conform to AWS naming conventions.
Tip
For more information, refer to Bucket naming rules.
Immutable Backup
By default, object-lock is enabled on buckets which means that objects are locked and cannot be deleted.
Toggle the switch if you want to disable this feature.
Click Continue.
The assistant displays all the automated configuration steps and the status for each step. The list of steps differs depending on the options chosen.
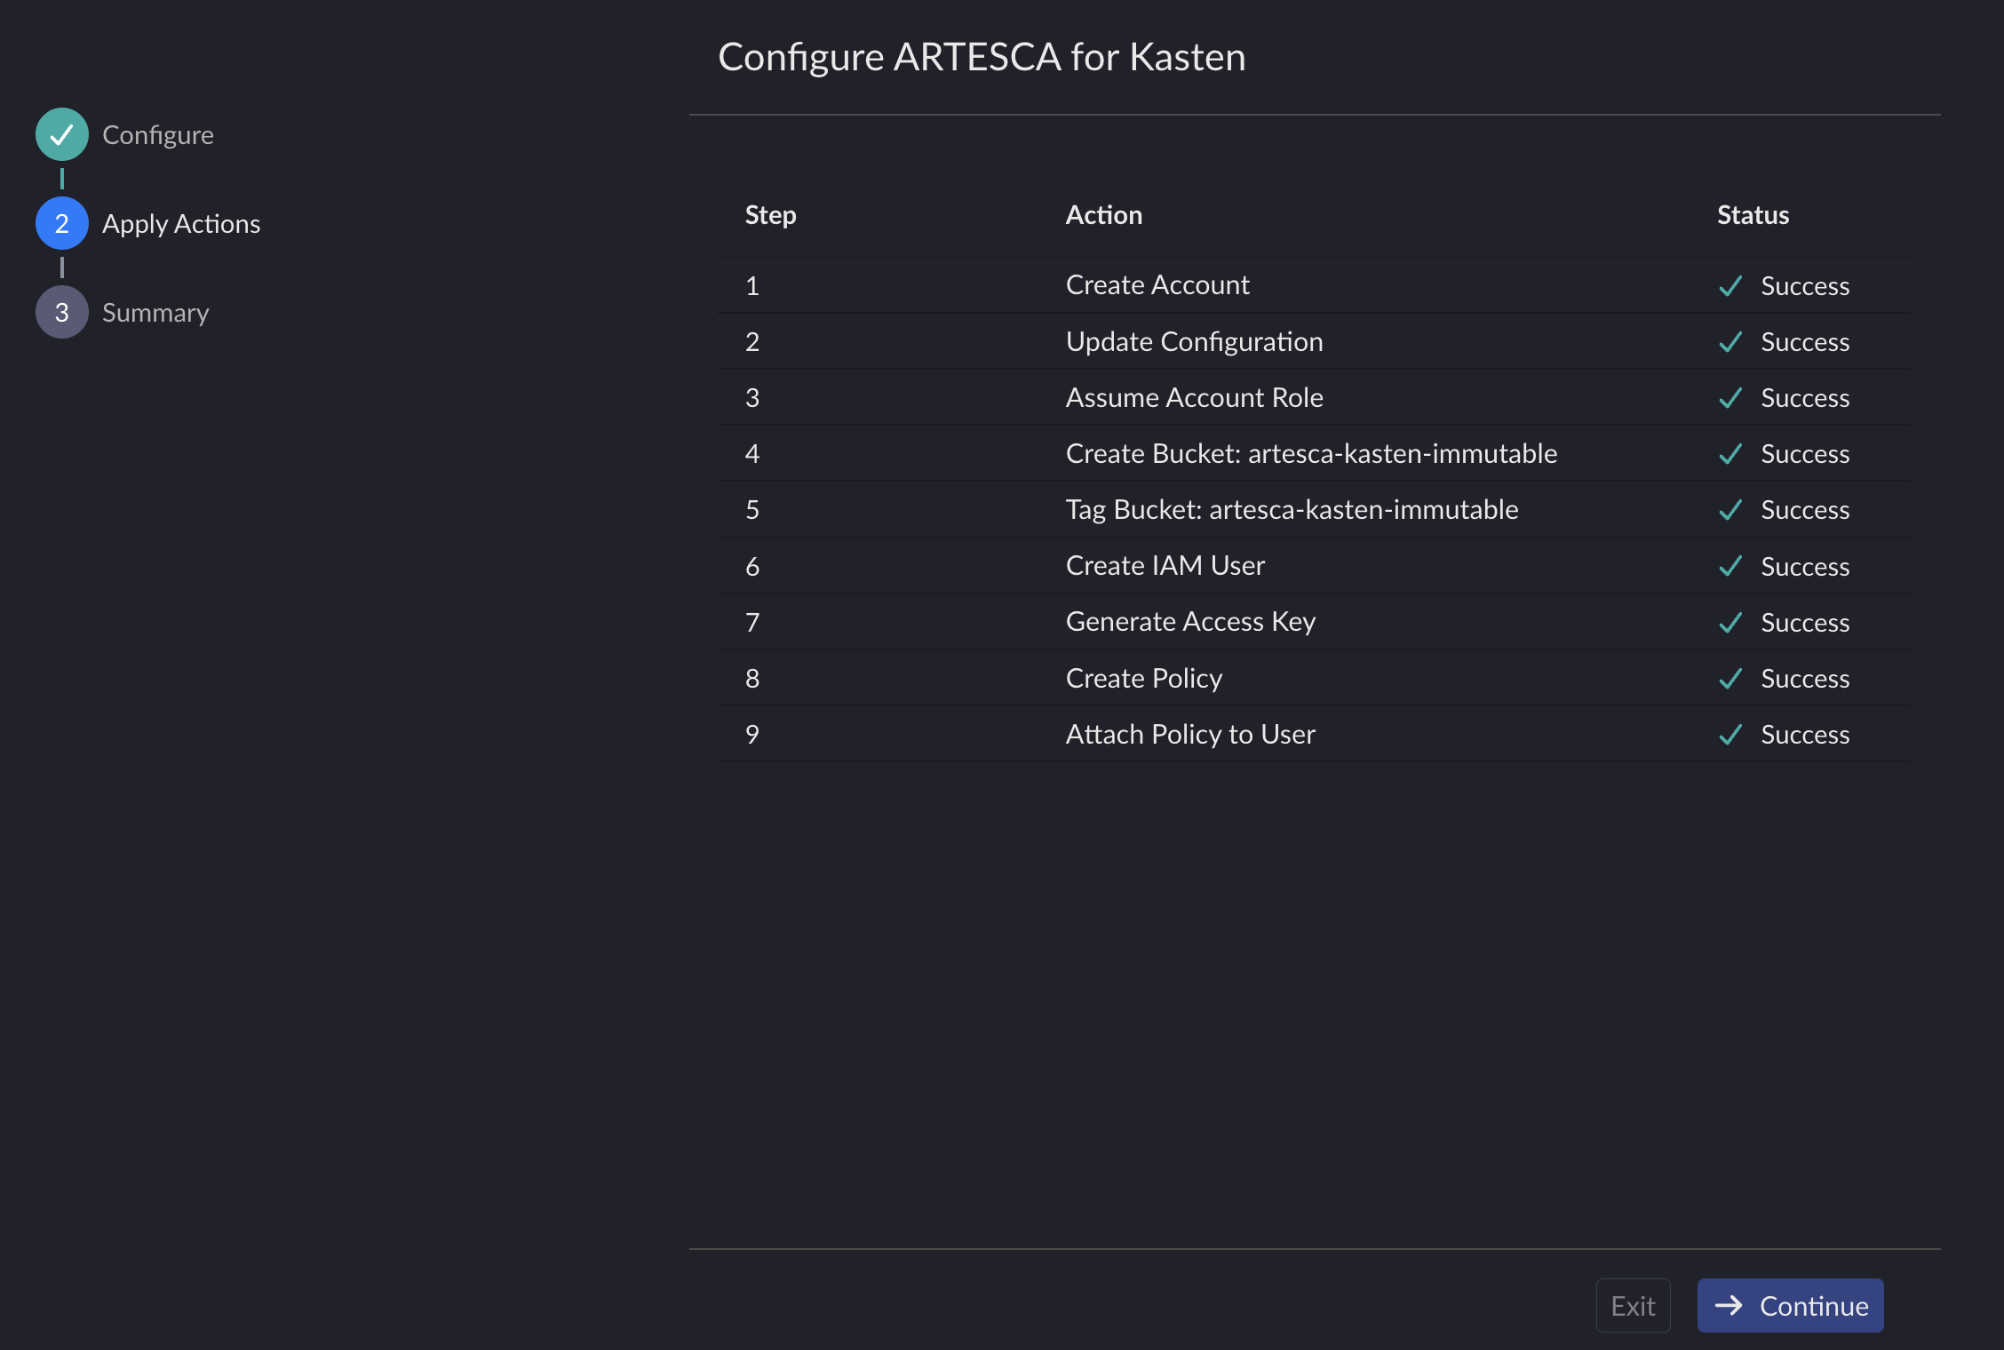
If a step fails, click Retry next to the corresponding step. If the step fails again, refer to Veeam Startup Assistant Fails for more information.
Note
If you decide to exit the assistant during a step failure, the resources created remain. If an account has been created and you want to restart the configuration, you must trigger the assistant manually from the Accounts page by clicking Start ISV Connector.
Click Continue once all the steps have succeeded.
The assistant displays the summary of the configuration.
Important
You need the information displayed in this page to complete the configuration in the Veeam Kasten application, so do not click Finish yet.
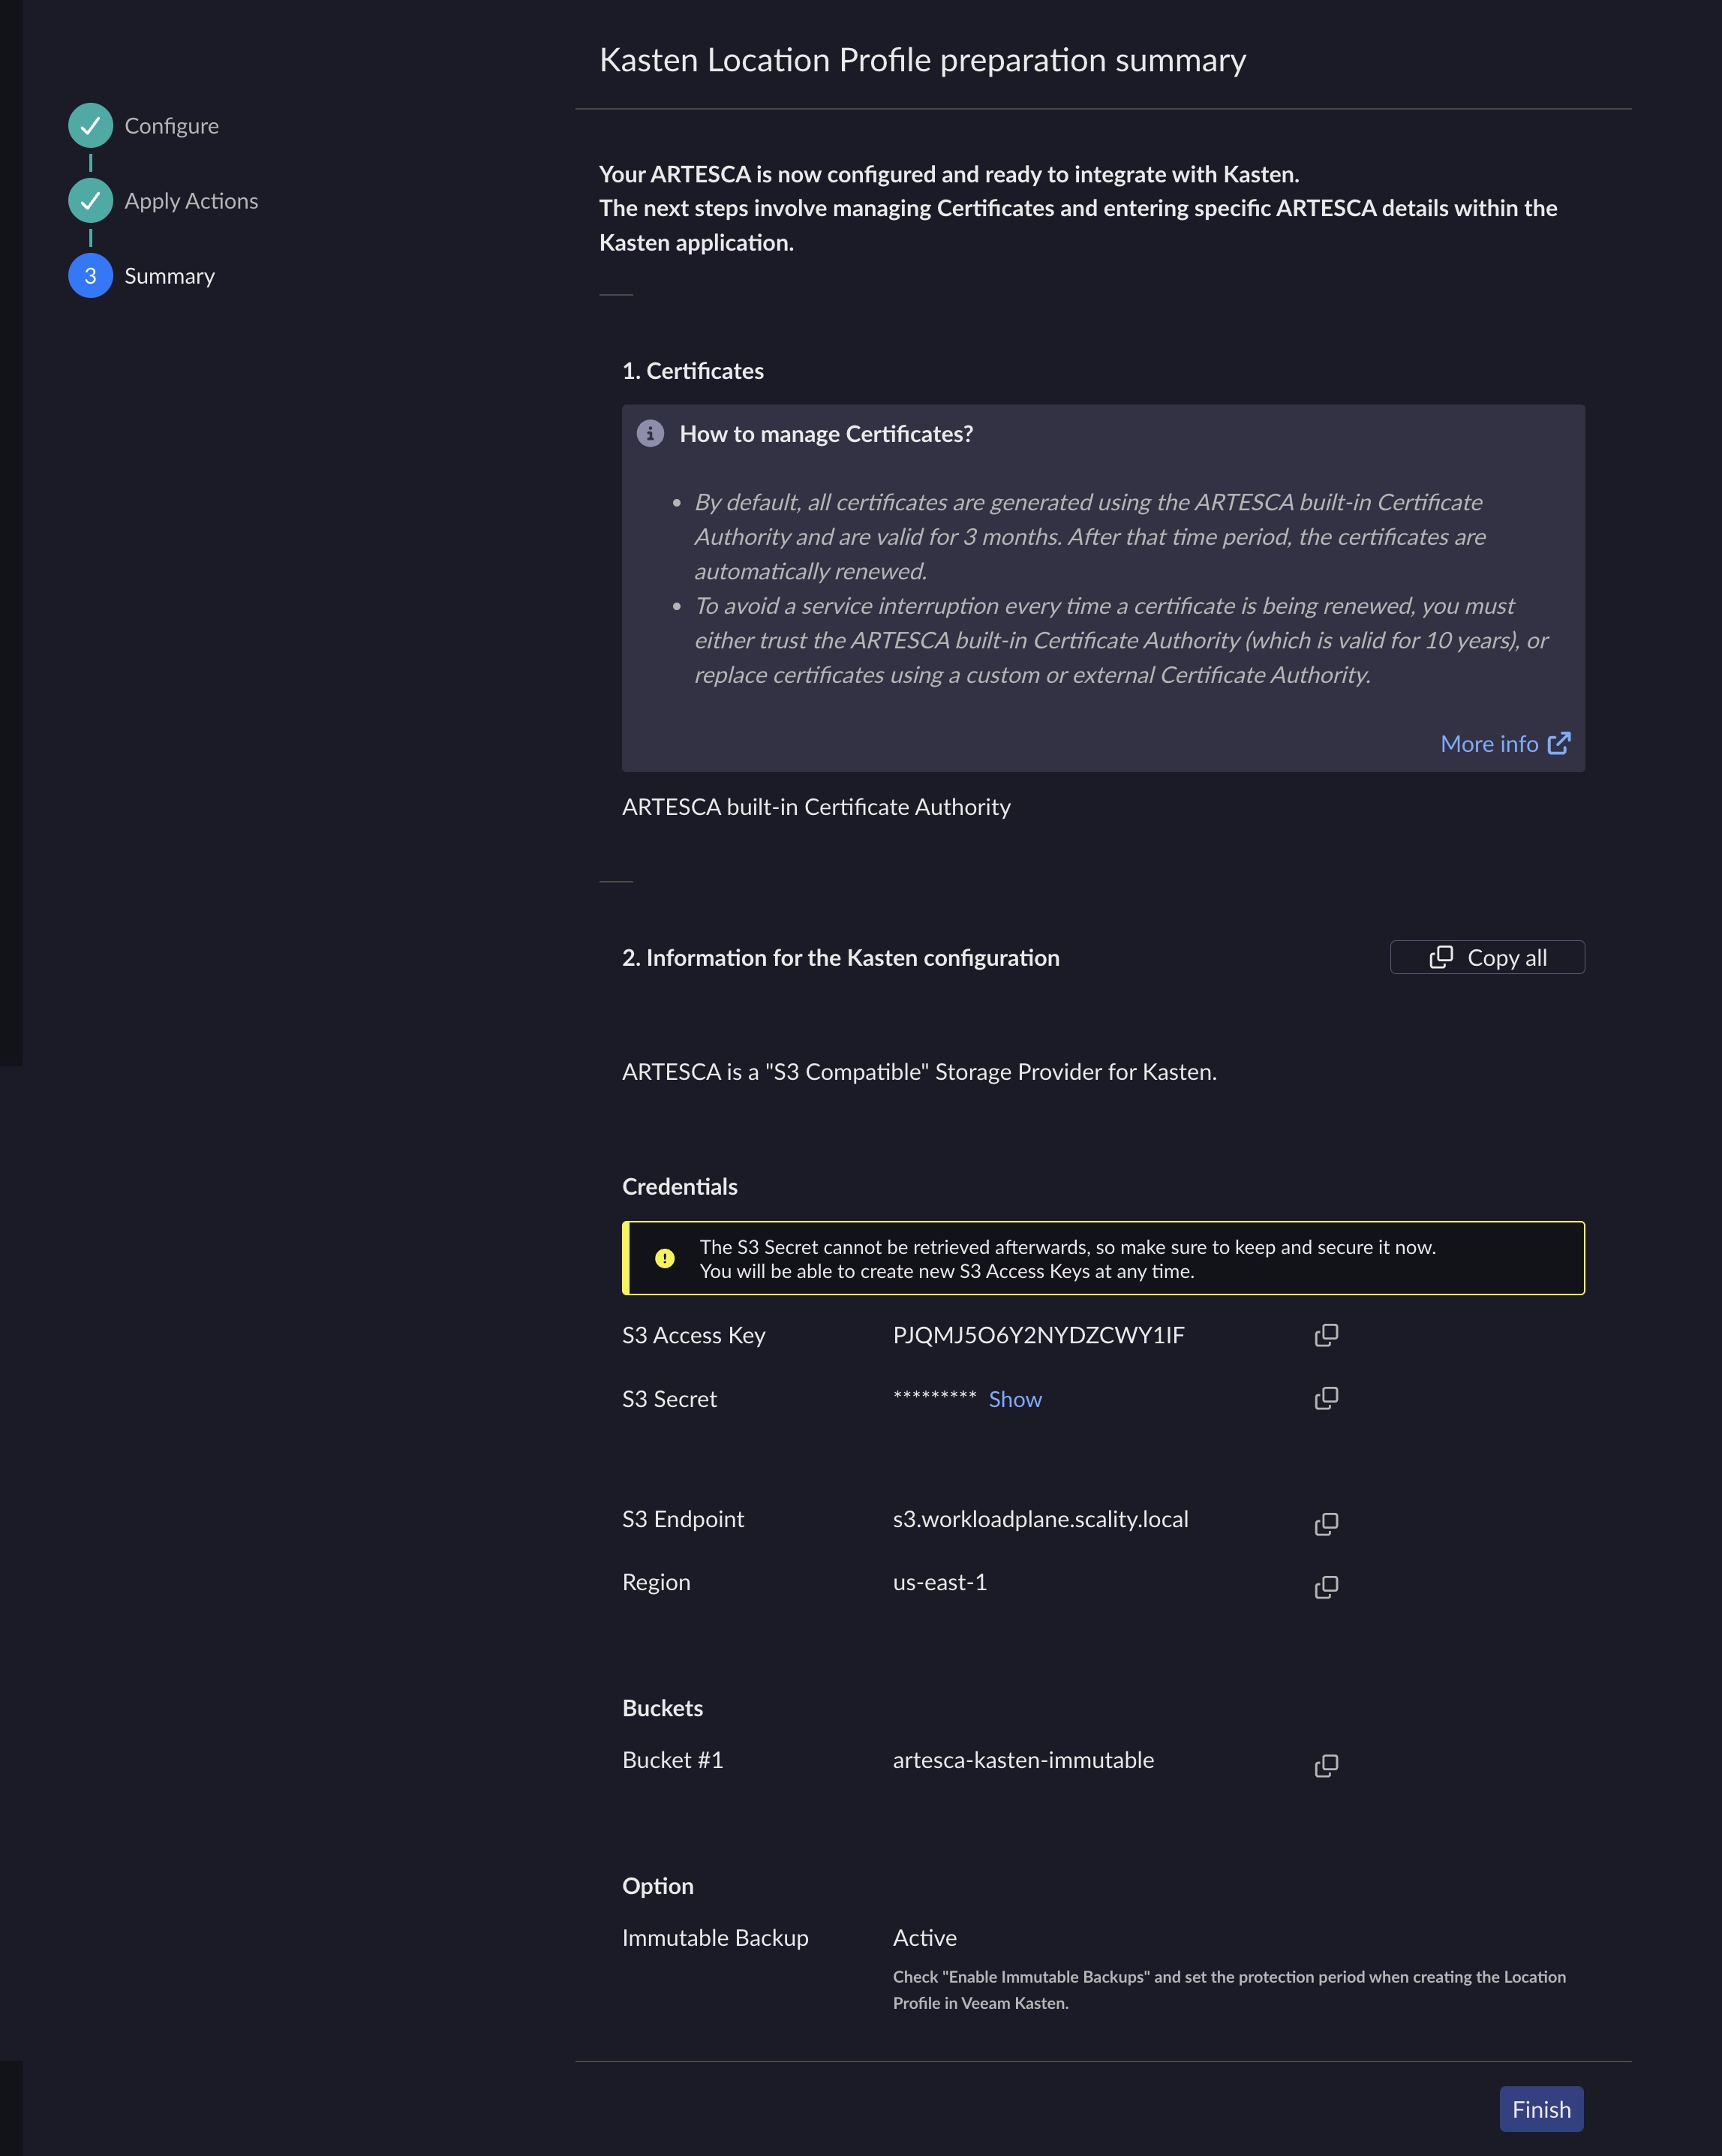
From the summary page, copy the different information one by one, or click Copy all to copy all the information at once.
Note
Scality recommends retrieving the information at this point as it is all grouped in one place. You can still retrieve some of the information later in the UI, but it will have to be done individually.
Besides, the secret key (if generated at this moment) is only available here. If you have not copied it, you will need to generate a new one later. Refer to Create IAM User Access Keys for more information.
Click Finish to close the assistant.
The resources created by the assistant (account, buckets, users, and policies) are available in the respective UI pages.
Note
The bucket created with the Veeam Kasten assistant is set for a specific use-case. To prevent mishandling, the Default Object-lock Retention option is disabled as this is managed by Veeam Kasten.
Note
Immutability in Veeam Kasten is enabled during Location Profile creation.
Create an Account for the Kasten application.
Create a Bucket to be used with Kasten application.
Create an IAM user for the Kasten application.
Create an IAM policy to grant the Kasten application access to the S3 repository and manage data from an object repository.
Note
Replace
bucketnamewith your bucket’s name.Immutable buckets
{
   "Version": "2012-10-17",
   "Statement": [
       {
           "Sid": "VisualEditor0",
           "Effect": "Allow",
           "Action": [
               "s3:GetBucketLocation",
               "s3:GetObject",
               "s3:PutObject",
               "s3:DeleteObject",
               "s3:GetBucketVersioning",
               "s3:GetBucketObjectLockConfiguration",
               "s3:ListBucketVersions",
               "s3:GetObjectVersion",
               "s3:GetObjectRetention",
               "s3:GetObjectLegalHold",
               "s3:PutObjectRetention",
               "s3:PutObjectLegalHold",
               "s3:DeleteObjectVersion"
           ],
           "Resource": [
               "arn:aws:s3:::bucketname/*",
               "arn:aws:s3:::bucketname"
           ]
       },
       {
           "Sid": "VisualEditor1",
           "Effect": "Allow",
           "Action": [
               "s3:ListAllMyBuckets",
               "s3:ListBucket"
           ],
           "Resource": "*"
       }
                  ]
}
Non-immutable buckets
{
   "Version": "2012-10-17",
   "Statement": [
       {
           "Sid": "SecureBucketPolicy0",
           "Effect": "Allow",
           "Action": [
               "s3:PutObject",
               "s3:GetObject",
               "s3:DeleteObject",
               "s3:GetBucketLocation",
               "s3:GetBucketVersioning",
               "s3:GetBucketObjectLockConfiguration"
           ],
           "Resource": [
               "arn:aws:s3:::bucketname/*",
               "arn:aws:s3:::bucketname"
           ]
       },
       {
           "Sid": "SecureBucketPolicy1",
           "Effect": "Allow",
           "Action": [
               "s3:ListAllMyBuckets",
               "s3:ListBucket"
           ],
           "Resource": "*"
       }
                 ]
}
Attach the IAM policy to the IAM user previously created.
Configure ARTESCA as a Non-immutable Location Profile
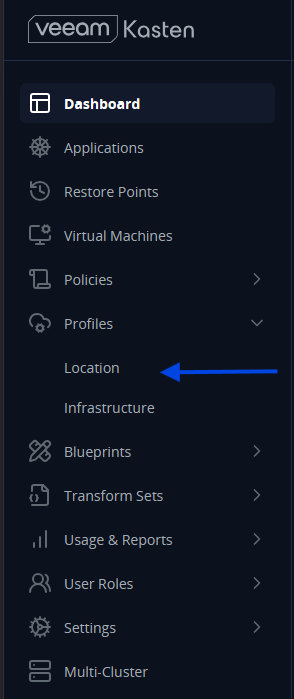
In the Veeam Kasten UI, on the sidebar, navigate to Profiles > Location.
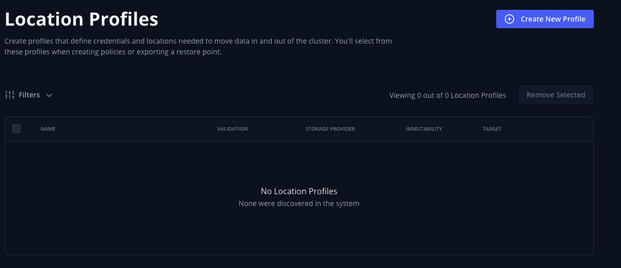
Click Create New Profile.
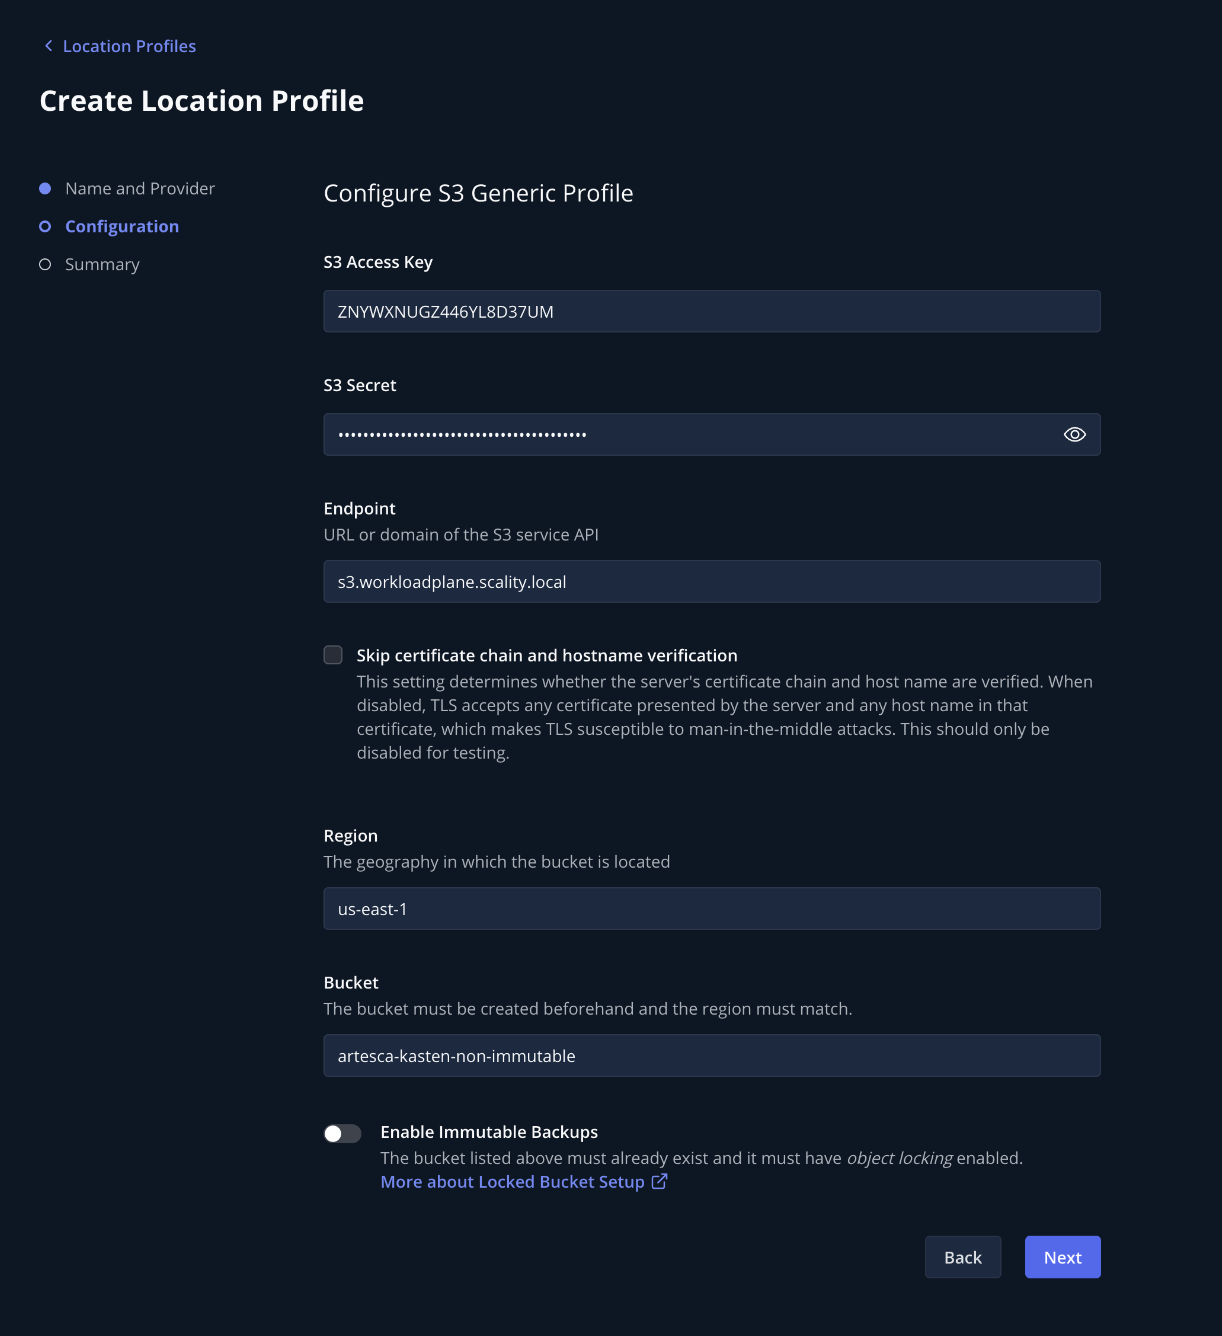
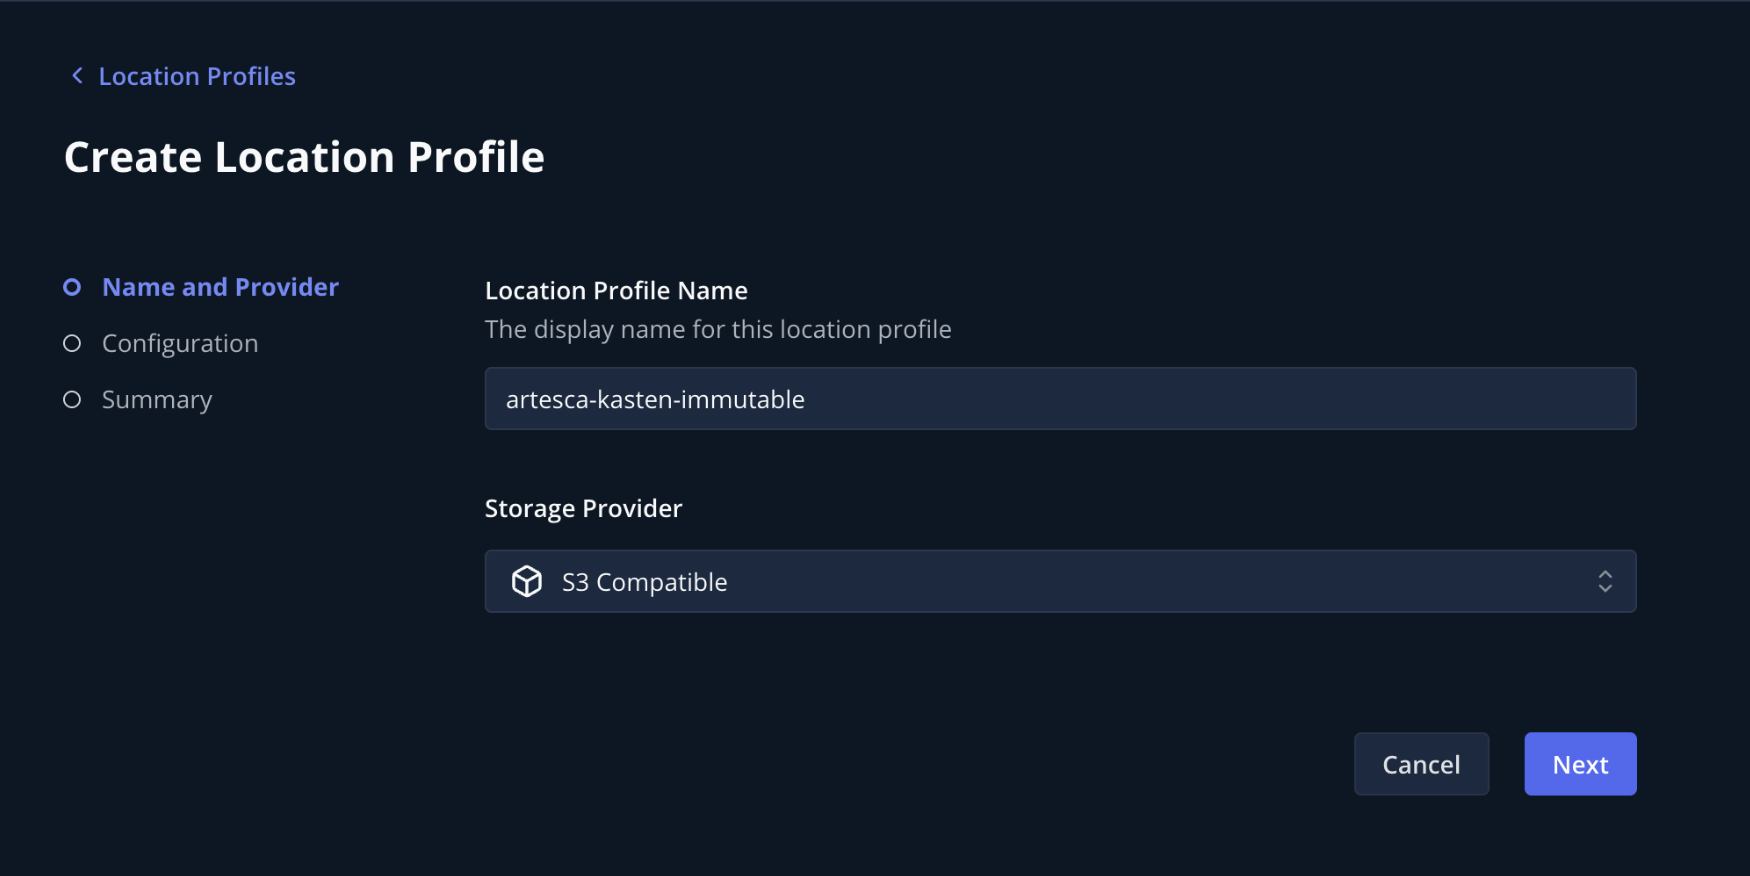
Specify a Location Profile Name and set the Storage Provider to S3 Compatible.

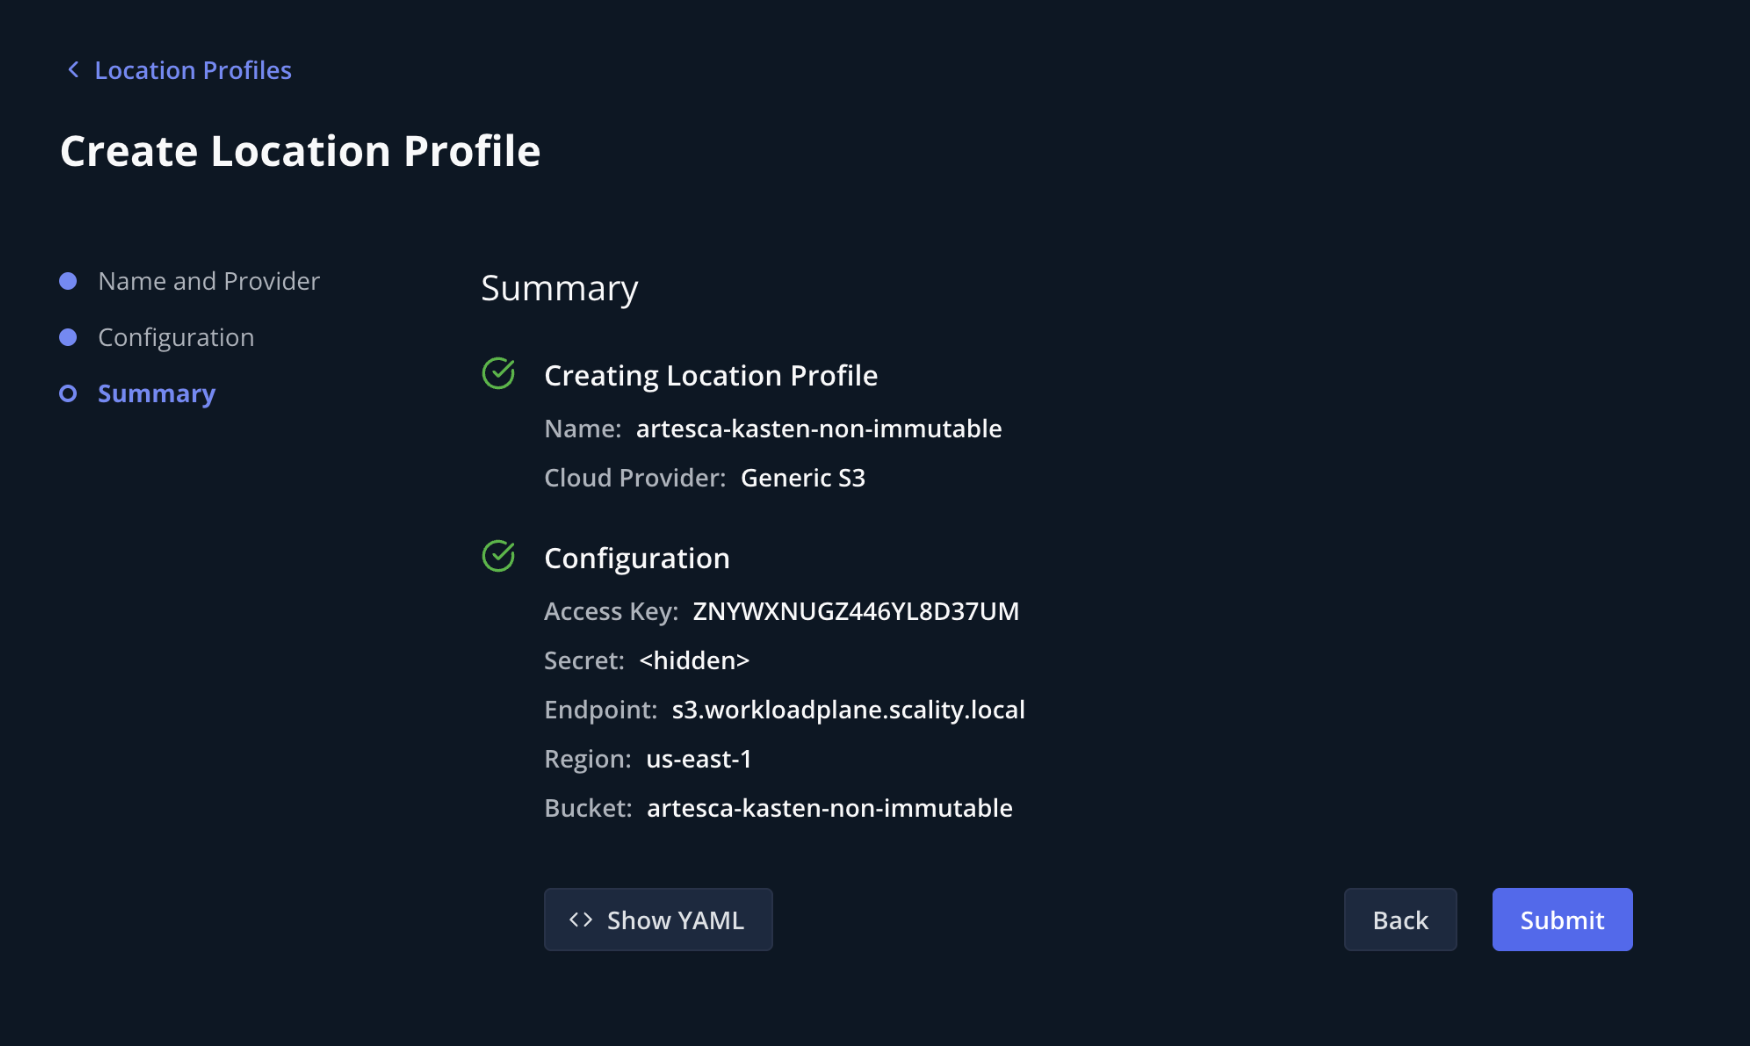
Enter credentials, endpoint, region and the bucket name, then click Next.
Note
The Enable Immutable Backups option must be left unchecked for non-immutable Location Profiles.
Click Submit to finalize the configuration.
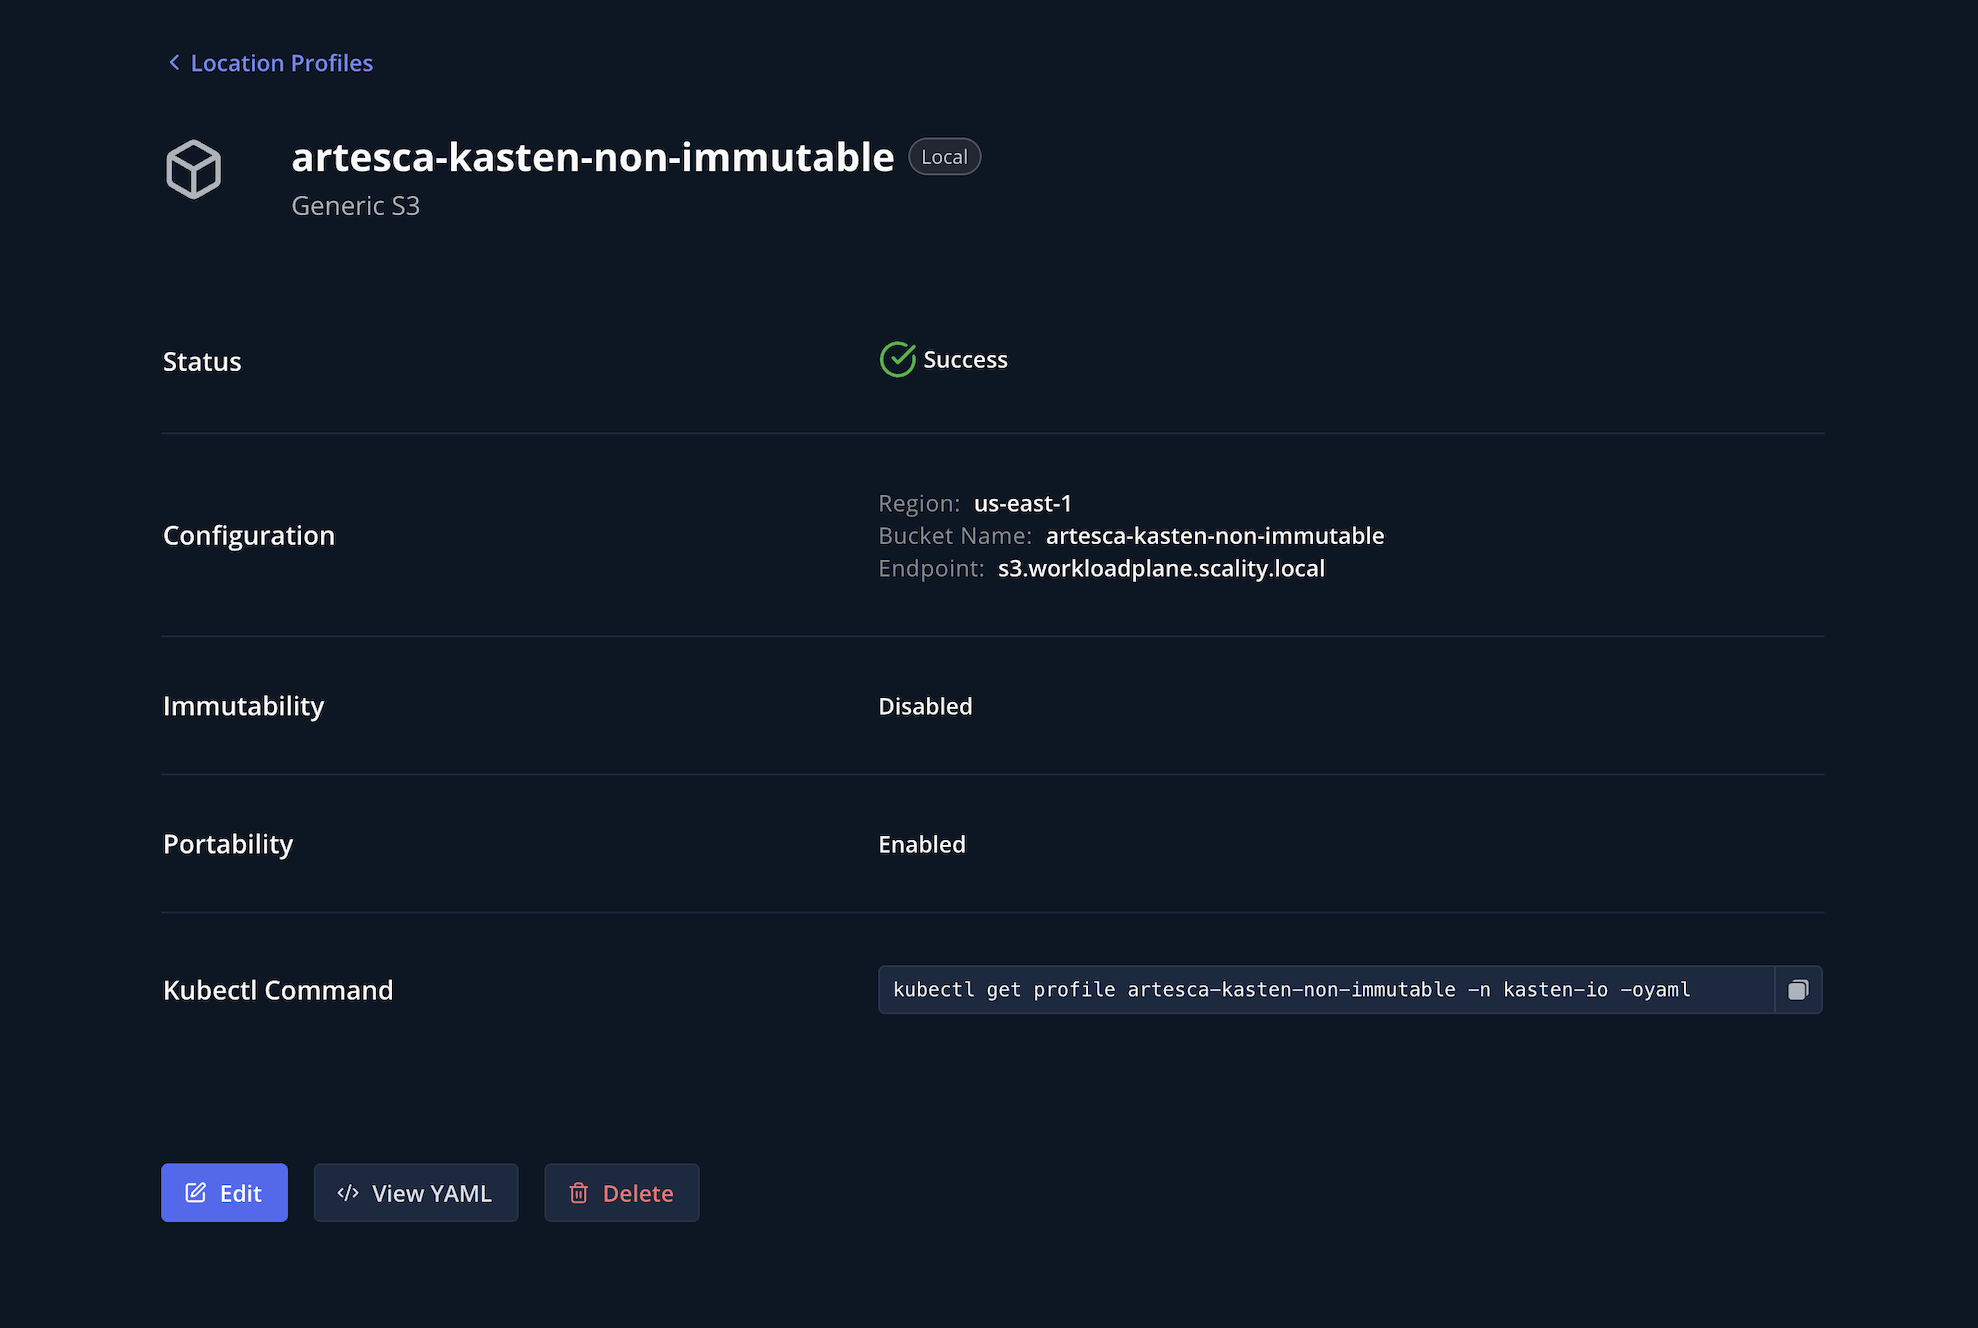
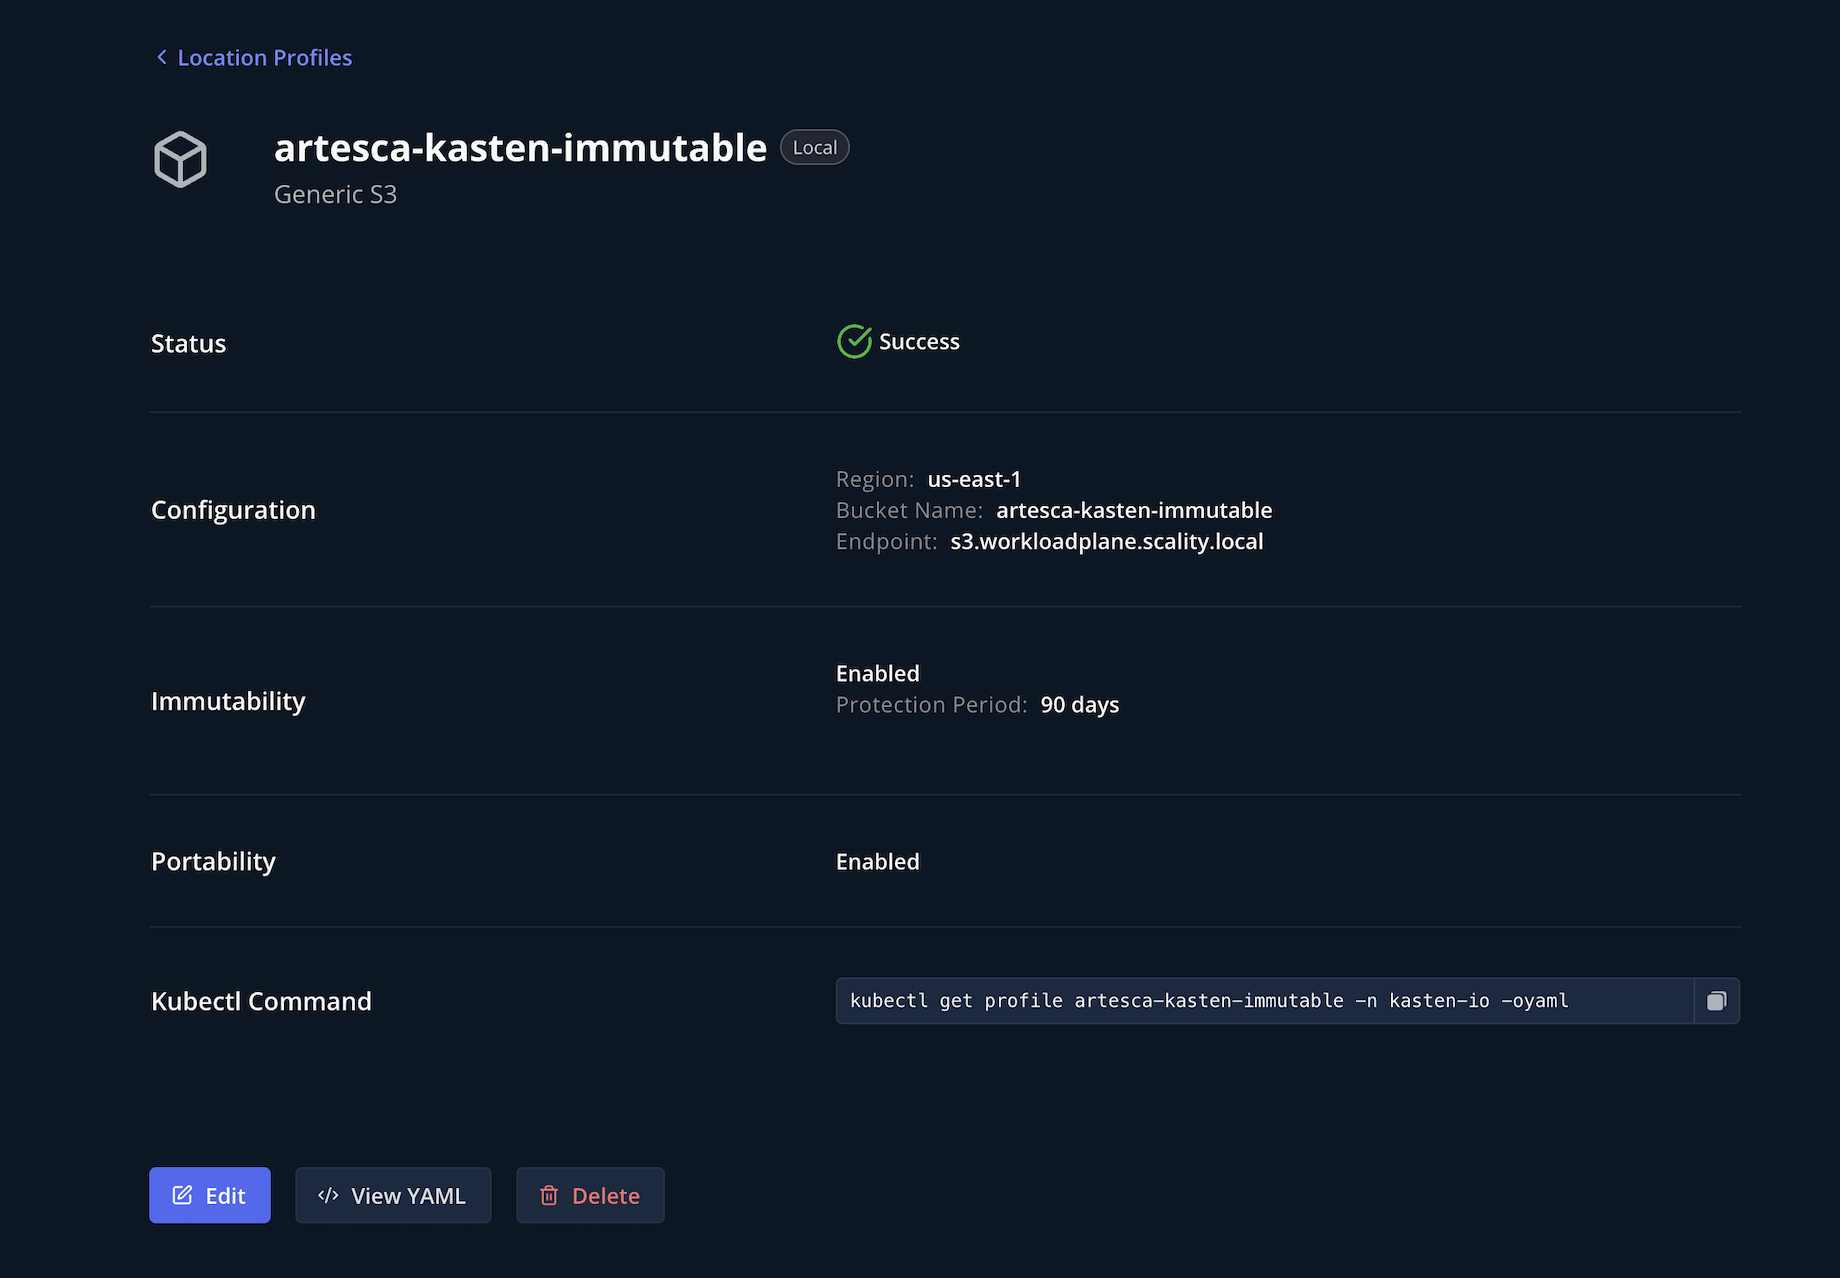
The newly created profile appears in the list of Location Profiles with a status as Success.
Configure ARTESCA as an Immutable Location Profile
In the Veeam Kasten UI, on the sidebar, navigate to Profiles > Location.
Click Create New Profile.
Specify a Location Profile Name and set the Storage Provider to S3 Compatible.
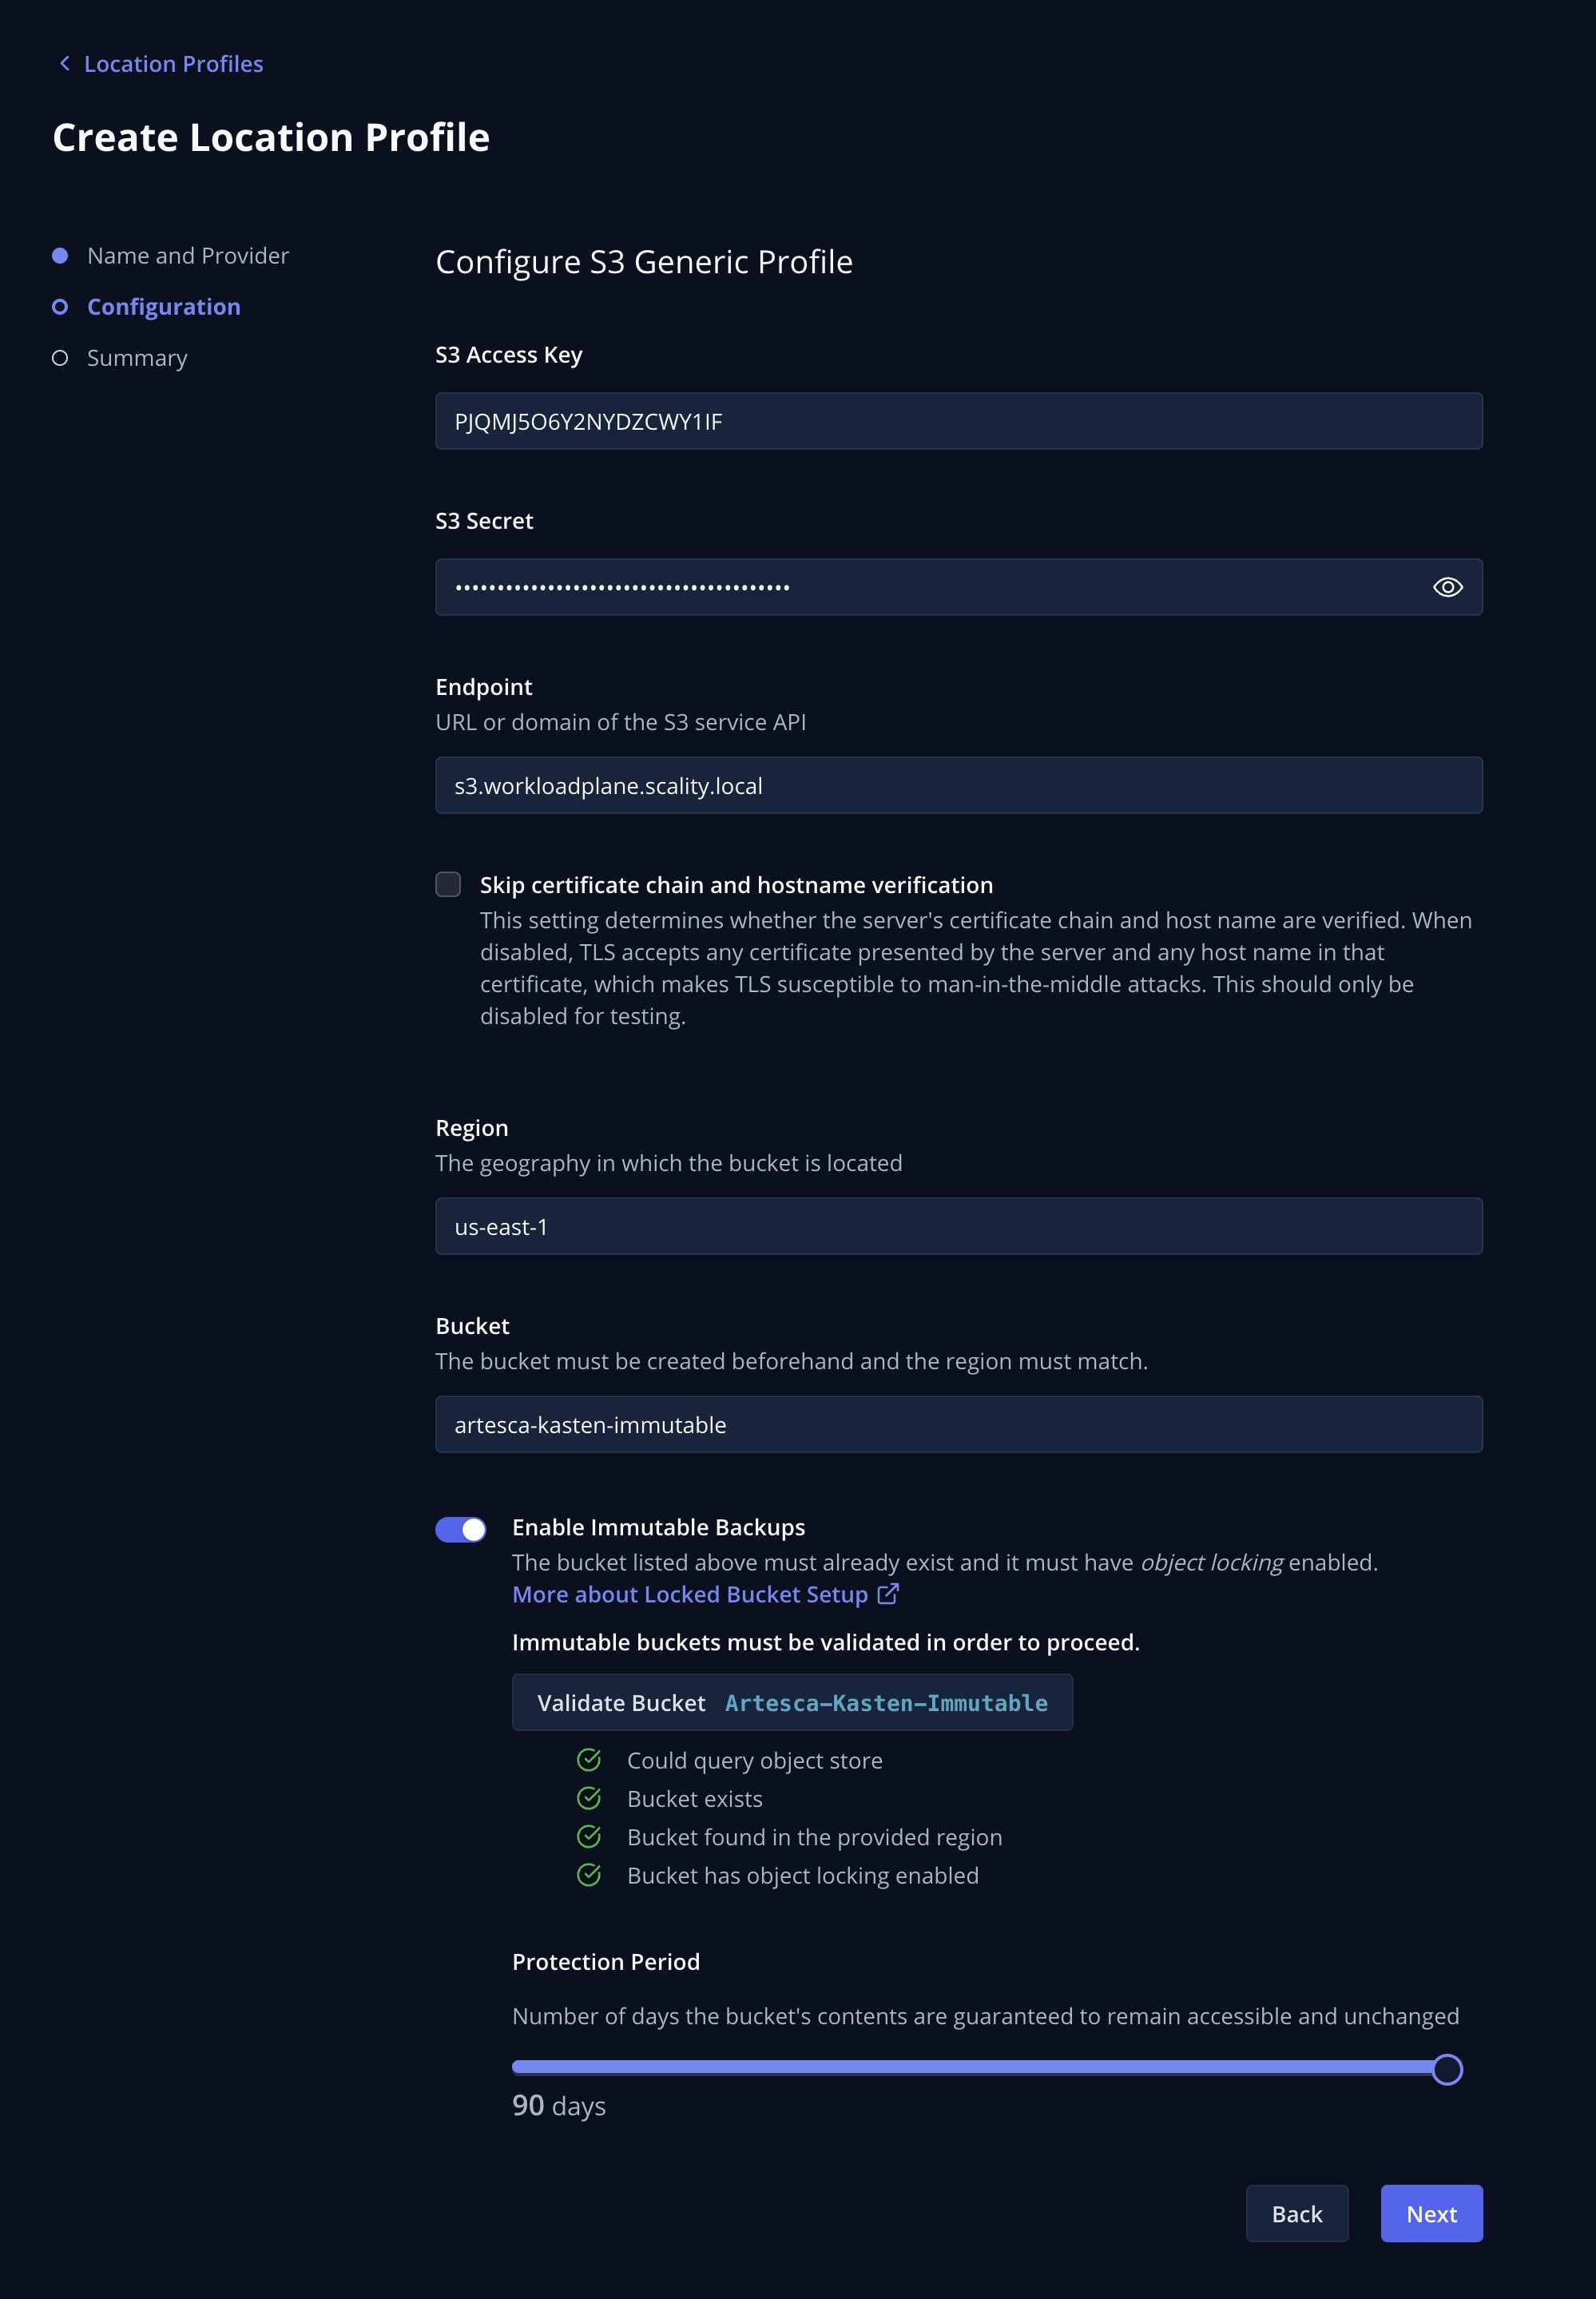
Enter credentials, endpoint, region and the bucket name.
Click Enable Immutable Backups. A new button, Validate Bucket displays to validate that the bucket meets the requirements. Click it to validate the bucket, and get a summary of the results.
Upon successful validation, enter the desired number of days for immutability protection.
Note
Veeam Kasten allows Protection Period set to a minimum of 1 day, and a maximum of 90 days.
Click Submit to finalize the configuration.
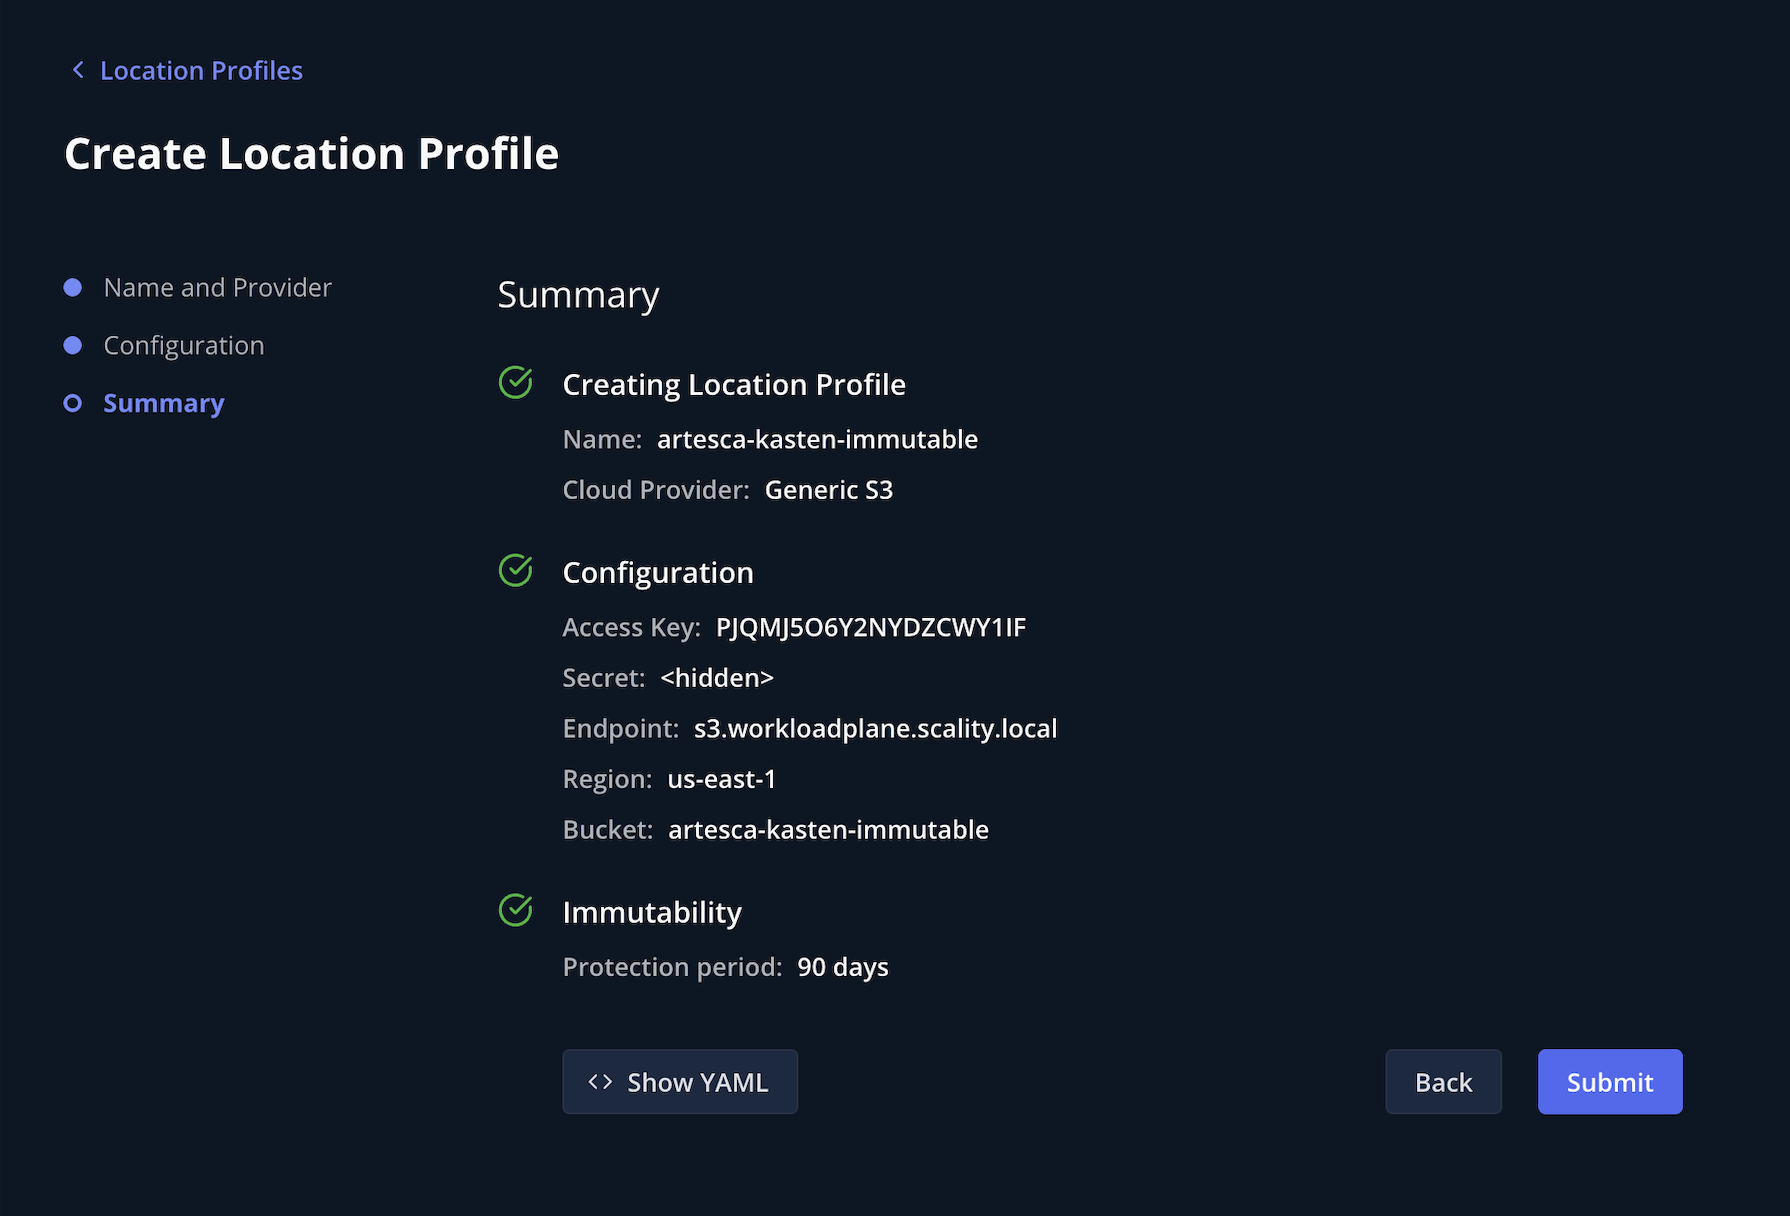
The newly created profile appears in the list of Location Profiles with a status as Success.
Create a Policy for Backups
This procedure allows you to create a policy for backups.
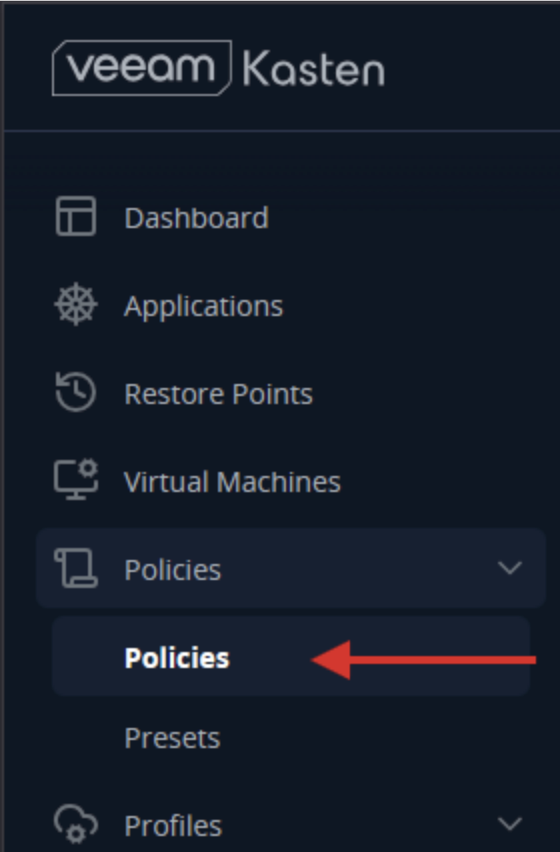
In the Veeam Kasten UI, on the sidebar, navigate to Policies > Policies and click Create New Policy.
Specify the following parameters:
Name: Display name for the policy.
Action: Select Snapshot.
Backup Frequency: Choose a desired backup frequency.
Enable Backups via Snapshots Exports: Enable this option to allow backups to be exported to ARTESCA.
Export Frequency: Choose the desired frequency to which backups need to be exported.
Export Location Profile: Choose the previously created Location Profile.
Retention of Exported Backups: Set a desired time period to retain exported backups in ARTESCA.
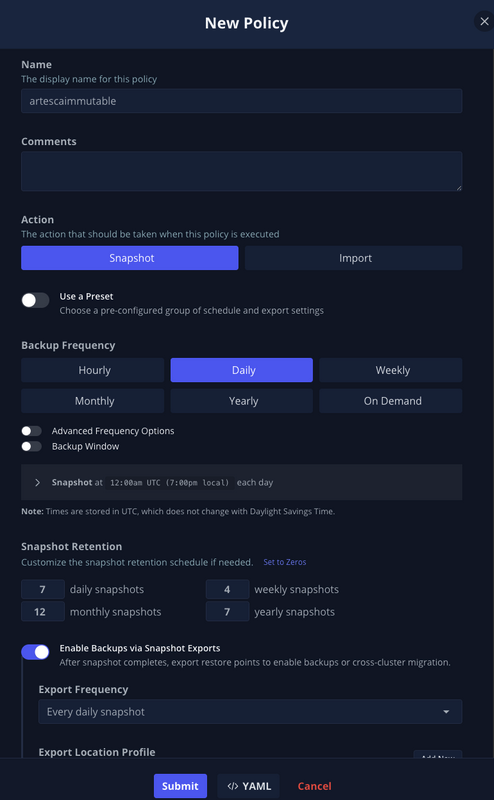
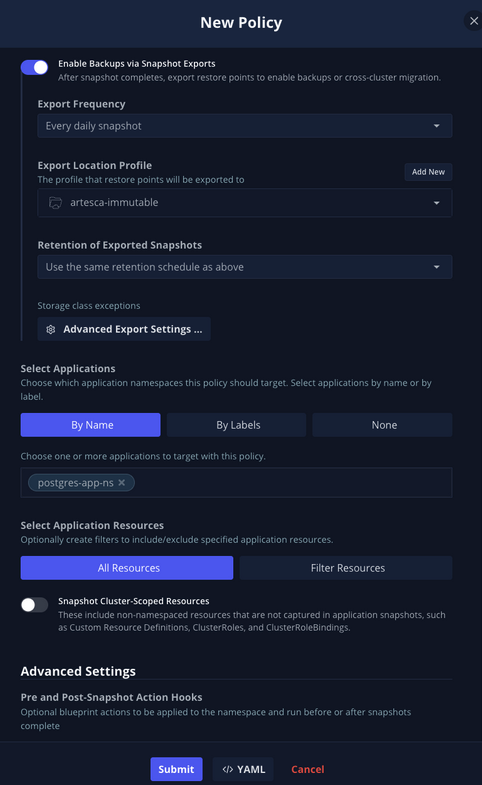
Click Submit to create the policy.