

Detach Policies
Prerequisites
You must have ARTESCA installed, refer to Deploy the ARTESCA Software Components.
Log in to the ARTESCA Identity Provider UI.
An IAM policy, refer Create IAM Policies.
An IAM policy attached to a user, group or role. Refer to Attach Policies.
Procedure
Click Data Management on the top menu and select Accounts on the left.
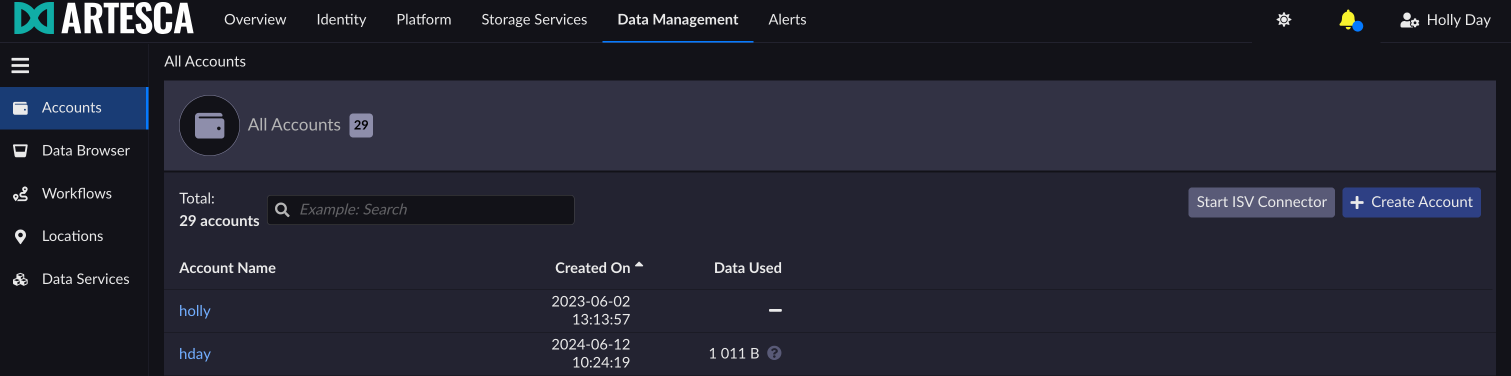
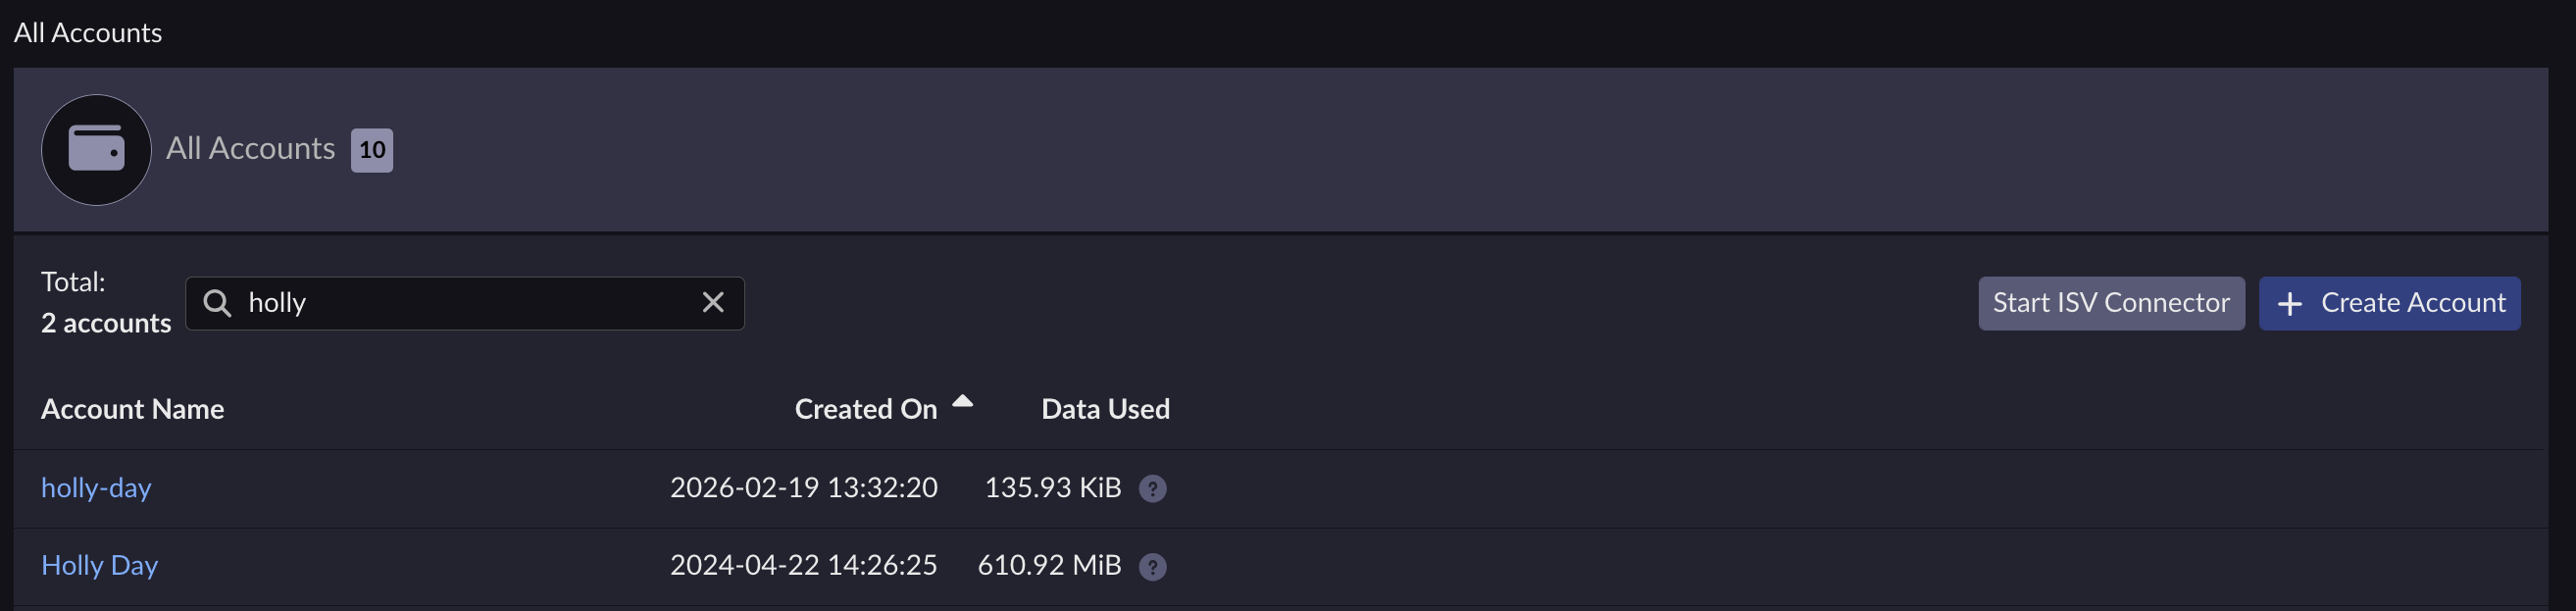
Select the account where you created your IAM Policy.
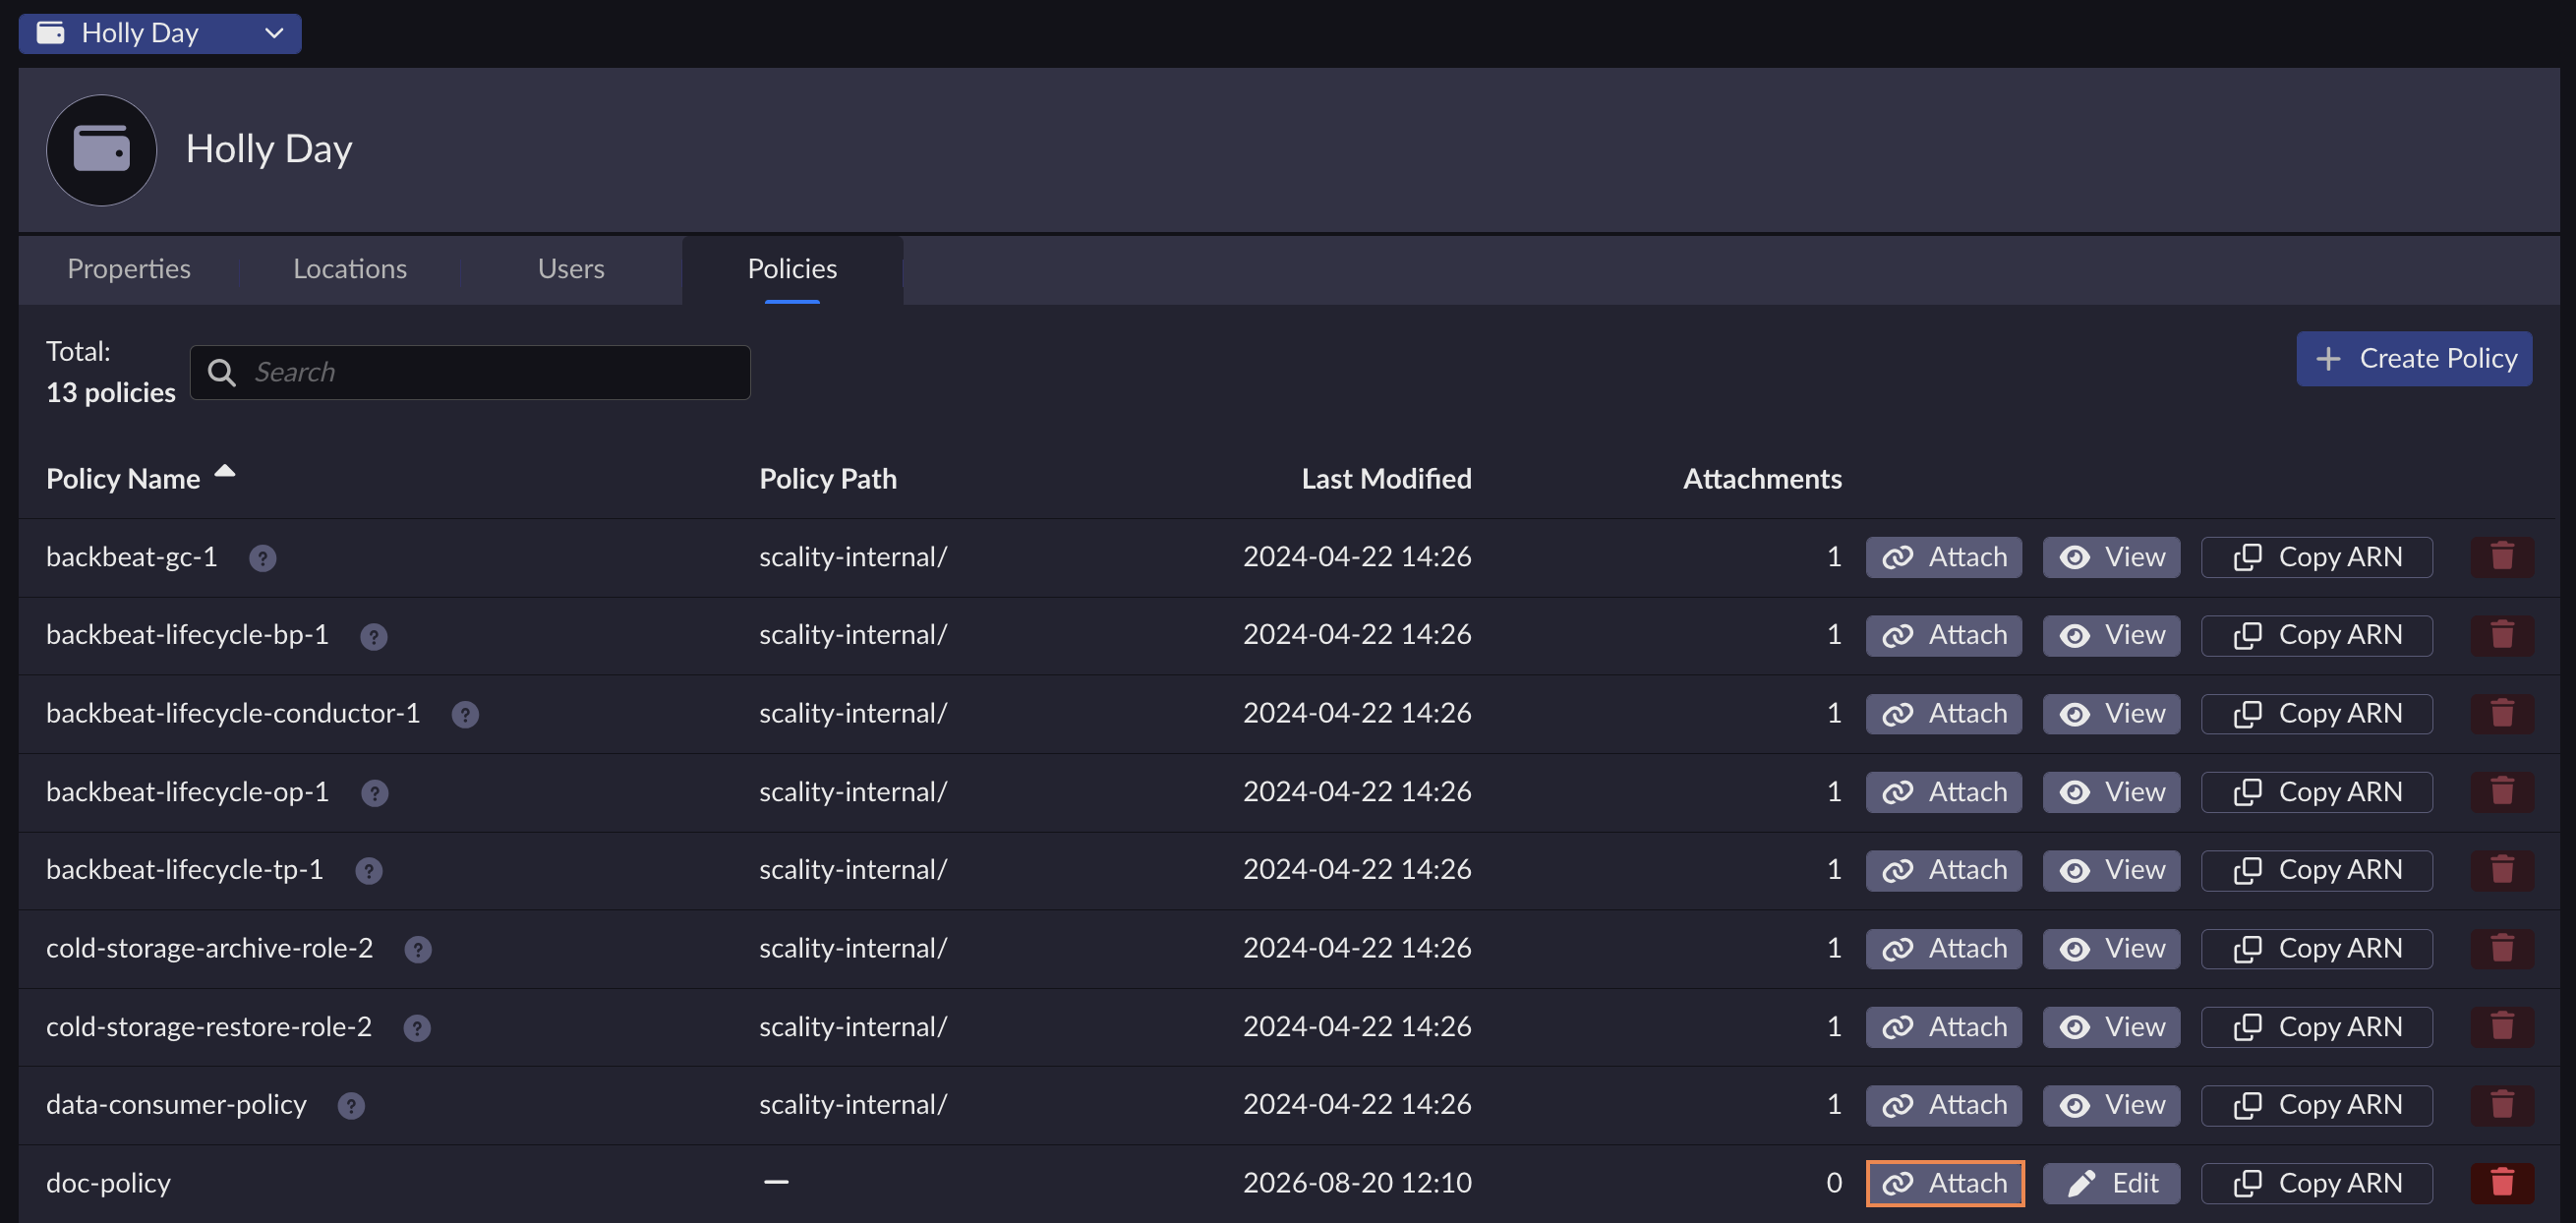
Under the Policies tab, select the policy to be detached, and click Attach.
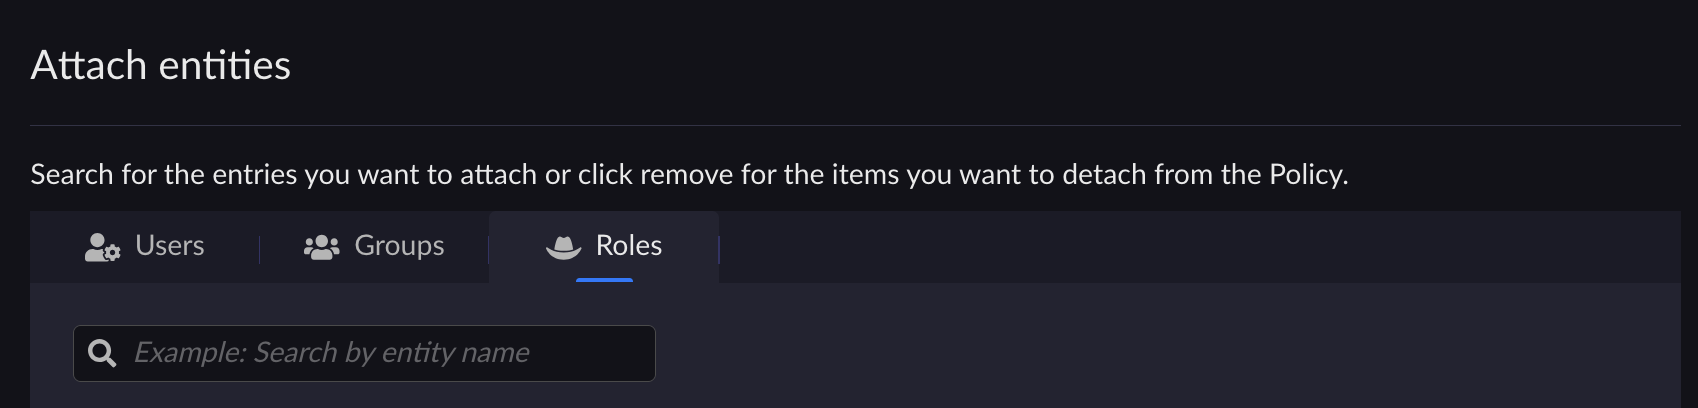
Select the type of identity Users, Groups or Roles and search for the entry you want to detach from the policy.
Click Remove to detach the policy.
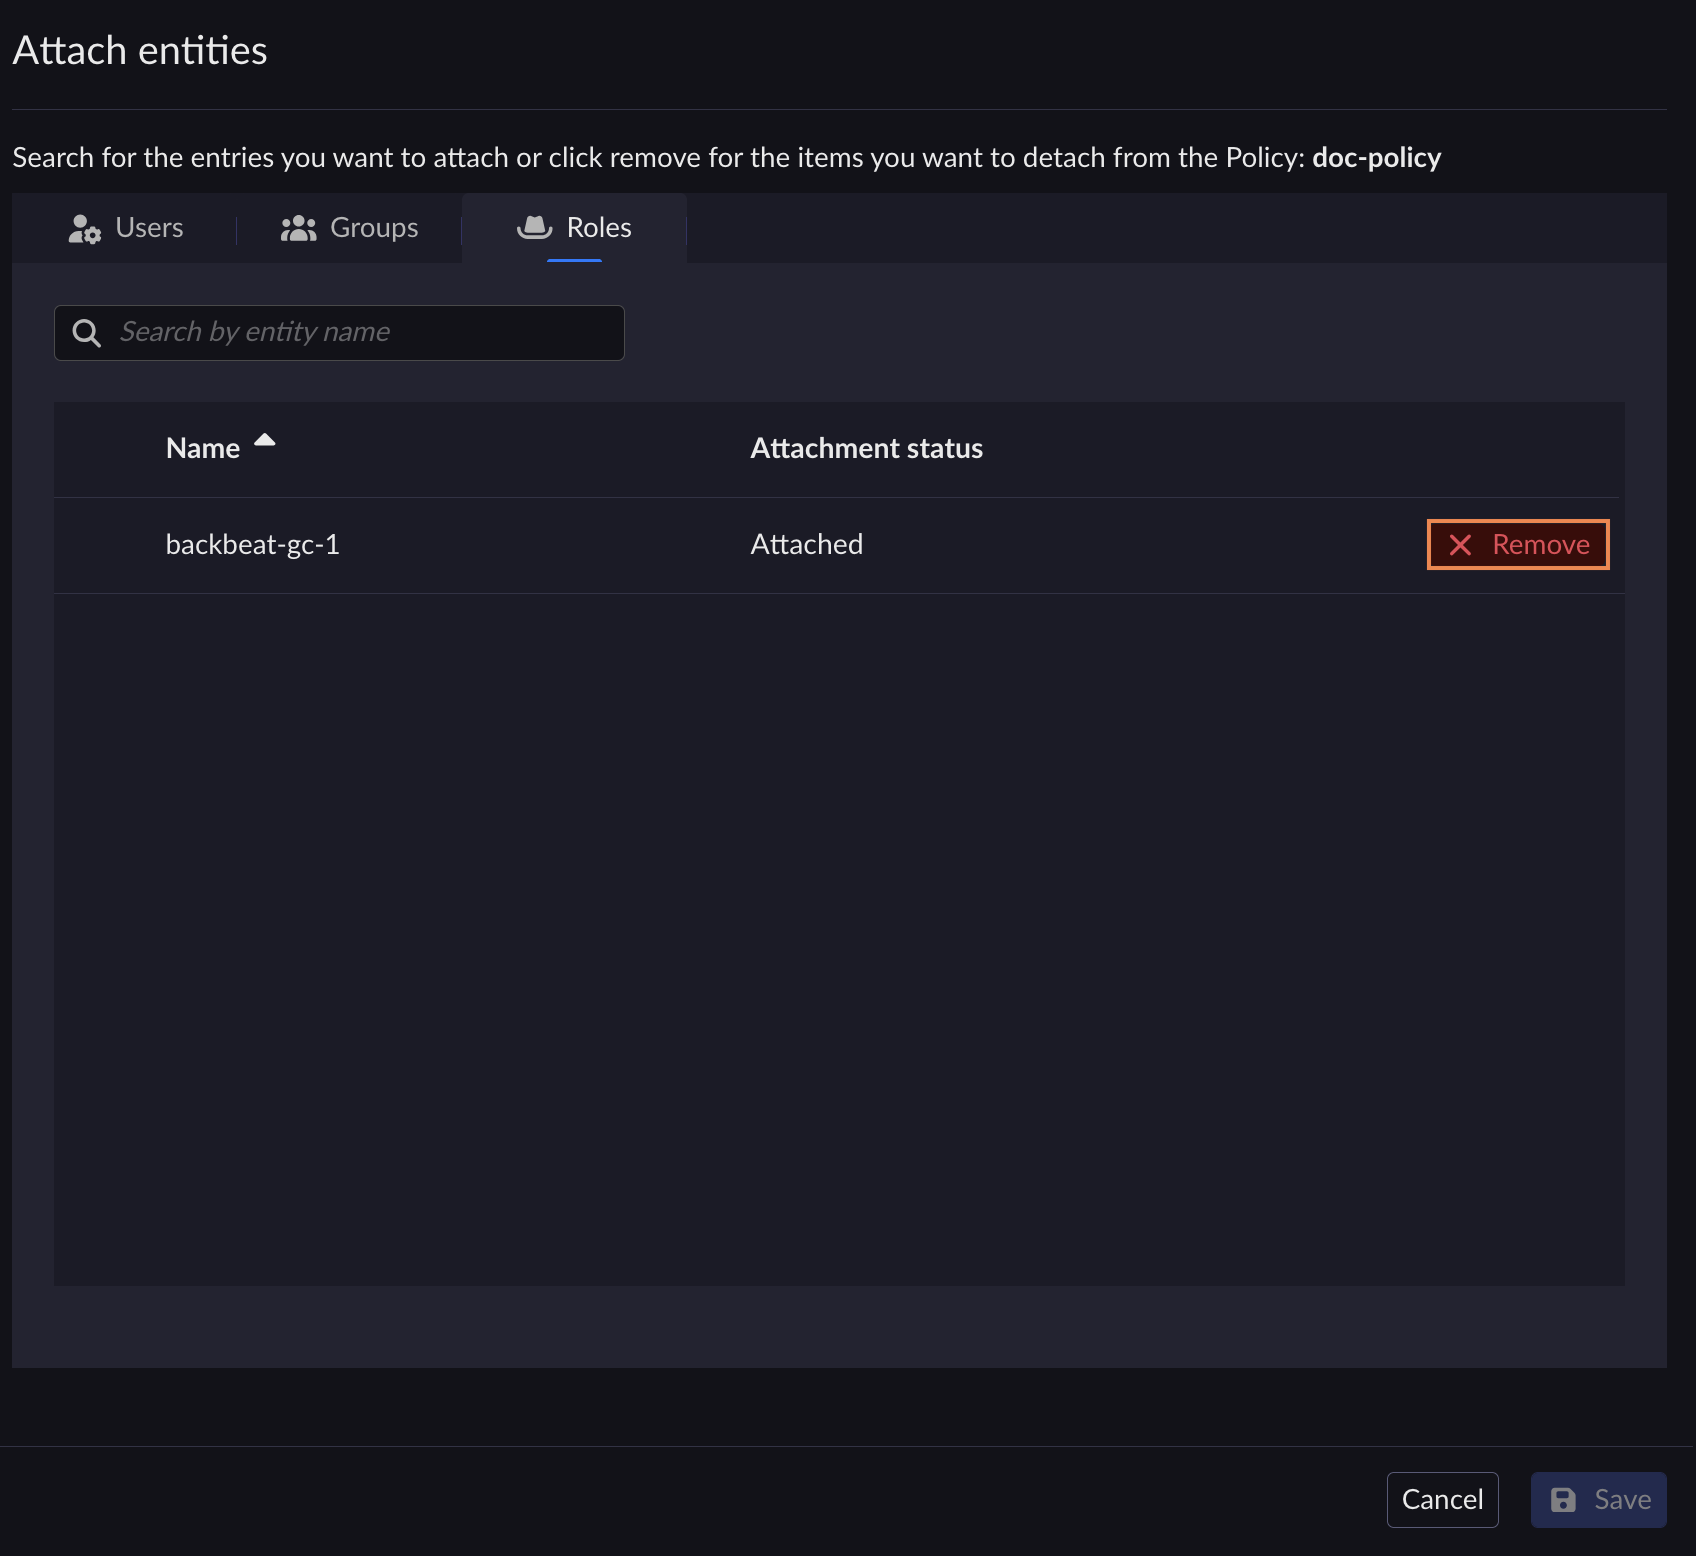
Click Save to confirm the detachment.
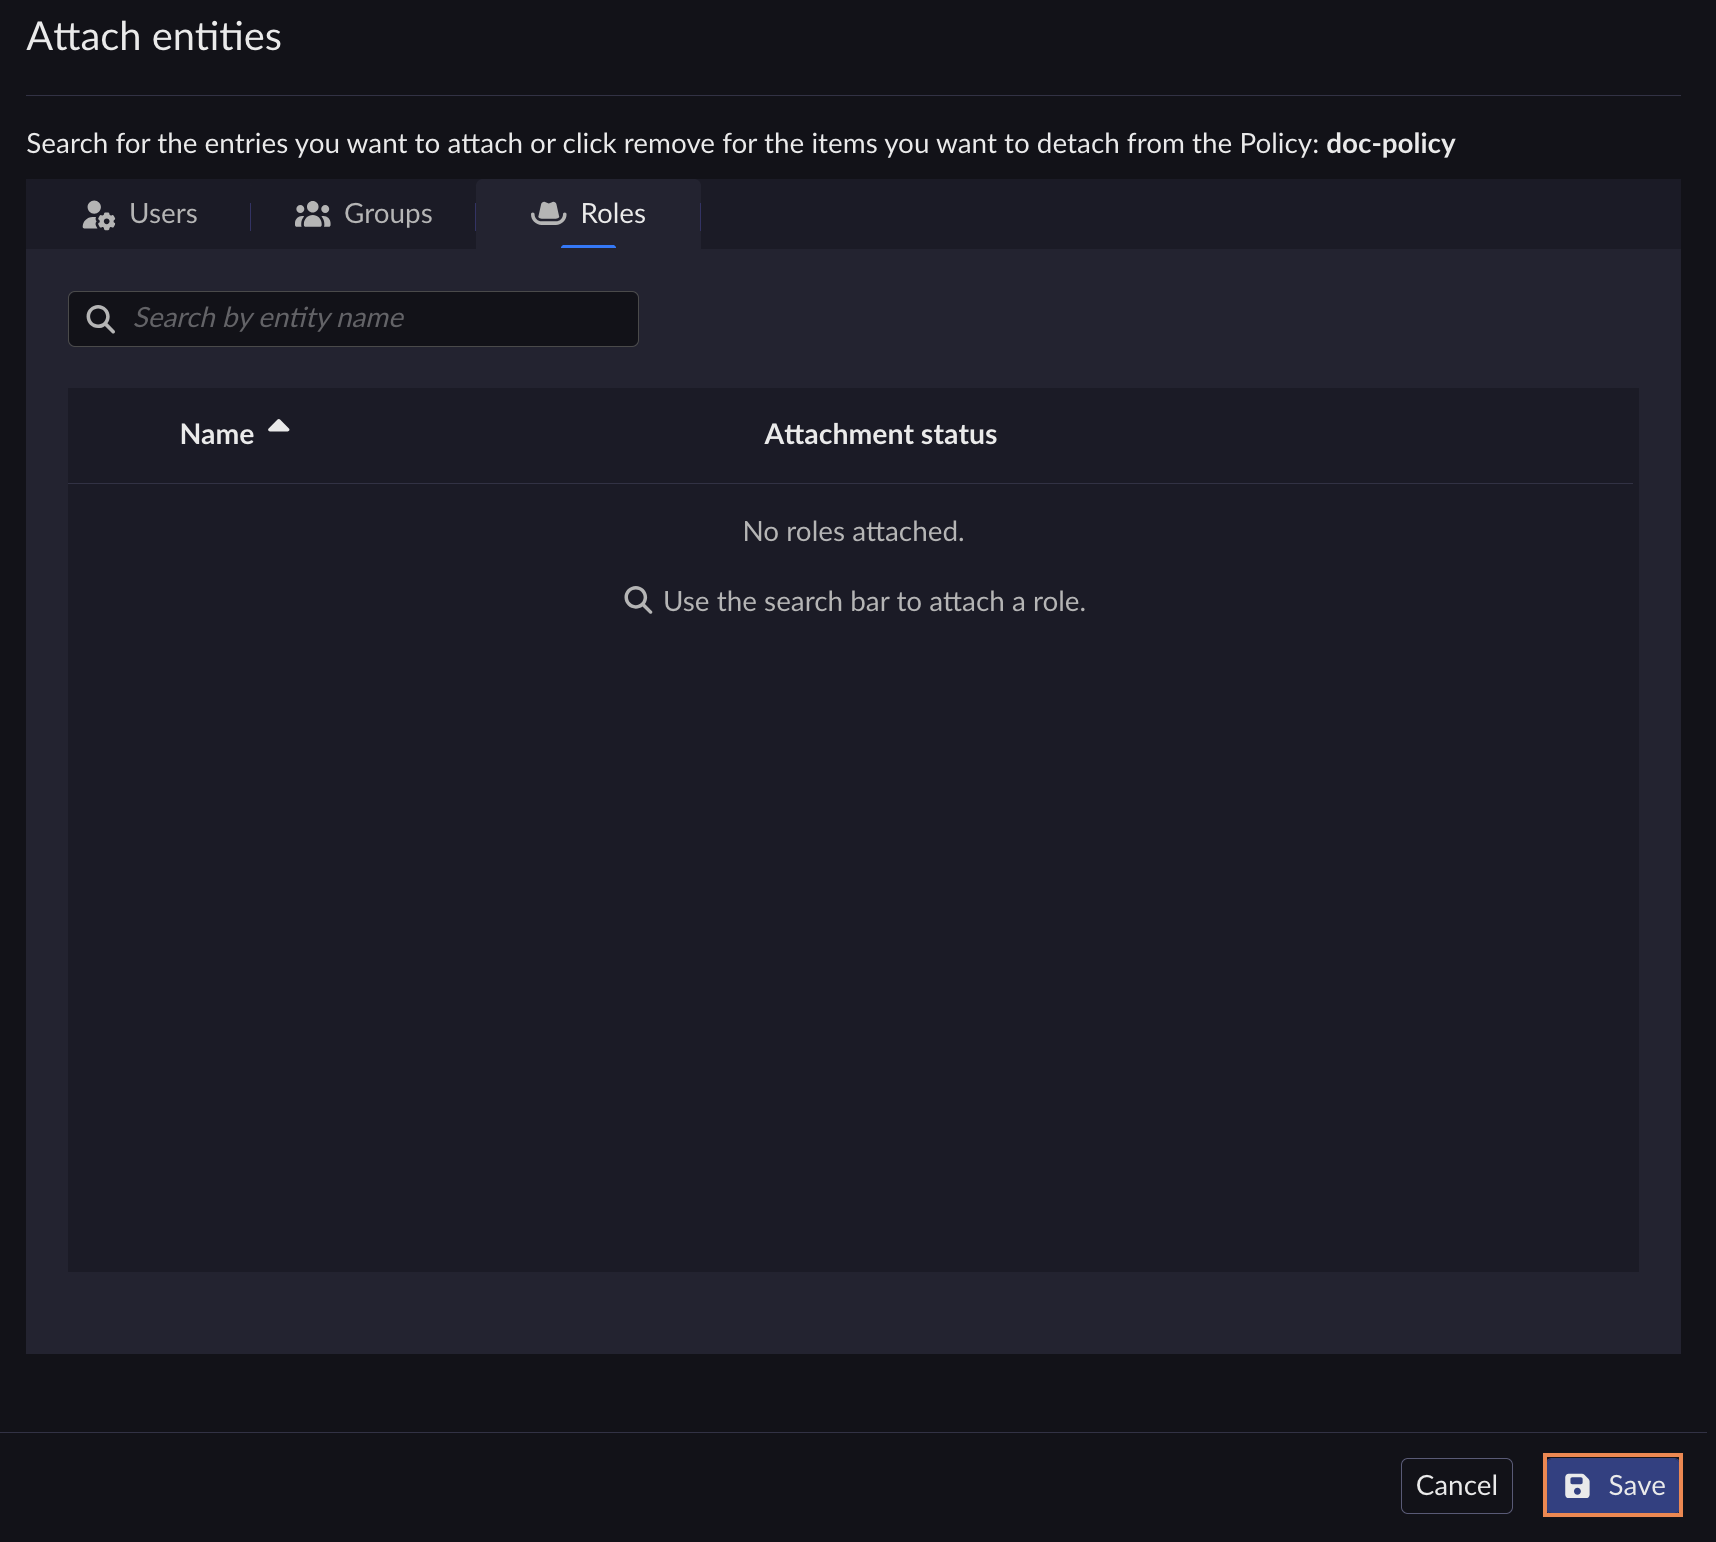
Click Confirm. The action type displays as Detach and the attachment status displays as Waiting for confirmation.
The attachment status switches to Success.
Note
Prior to calling these CLI commands, you must first obtain policy ARN. Refer to List IAM Policies for more information.
Note
To retrieve the ARN when the policy name is known, where ExamplePolicy is the
name of the created policy, issue the following command:
aws --endpoint-url https://iam.<base-domain-name> \
iam list-policies --query 'Policies[?PolicyName==ExamplePolicy].Arn' \
--no-paginate --output text
To detach a group policy run the command:
aws --endpoint-url https://iam.<base-domain-name> \
iam detach-group-policy --group-name my-group --policy-arn \
arn:aws:iam::123456789012:policy/ExamplePolicy1
To detach a role policy run the command:
aws --endpoint-url https://iam.<base-domain-name> \
iam detach-role-policy --role-name my-role --policy-arn \
arn:aws:iam::123456789012:policy/ExamplePolicy1
To detach a user policy run the command:
aws --endpoint-url https://iam.<base-domain-name> \
iam detach-user-policy --user-name my-user --policy-arn \
arn:aws:iam::123456789012:policy/ExamplePolicy1


