

AD/LDAP Federate Authentication
Lightweight Directory Access Protocol (LDAP) is a widely-used protocol that enables applications to query and manage user information stored in a directory service. LDAP serves as a central point to authenticate users and manage their permissions, ensuring that they can use the same set of credentials across different services.
LDAP Integration with ARTESCA
Configuring LDAP allows users managed by directory services like Active Directory (AD) to authenticate within ARTESCA. By connecting LDAP to the ARTESCA identity manager, user and group data from LDAP will be available within the IdentityUI.

ARTESCA supports connecting multiple identity providers simultaneously and will search across all integrated sources when a user attempts to log in.
Role-Based Authentication
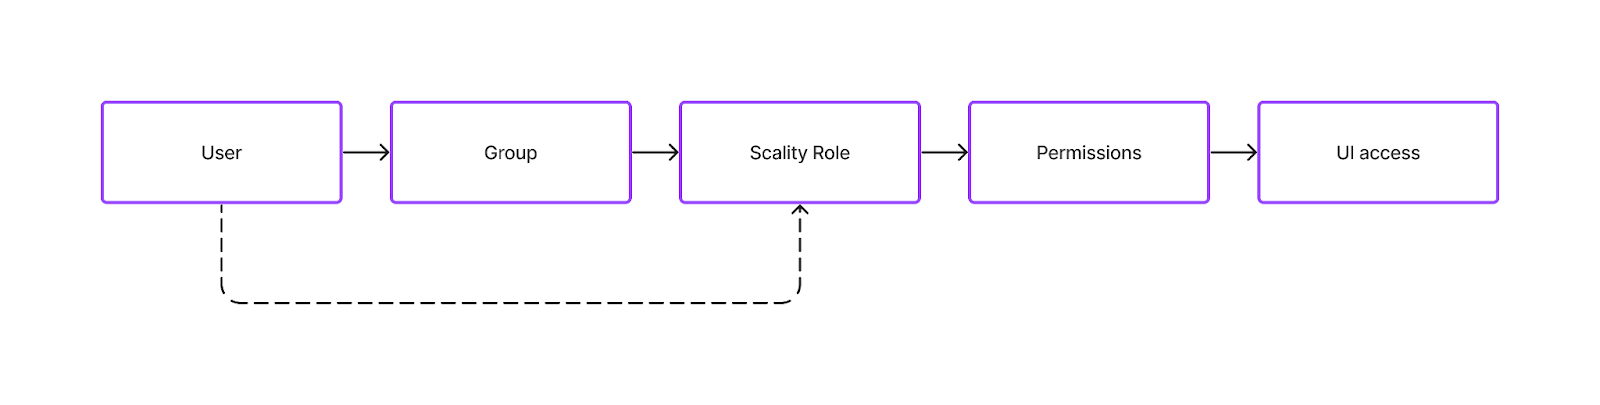
Role-based authentication determines user permissions, allowing for roles that are either directly assigned or inherited based on LDAP group membership. With LDAP integration, authentication is driven by users’ group affiliations in AD/LDAP, assigning roles that are specific to each LDAP group. Such a strategy ensures that user permissions within ARTESCA are in strict accordance with organizational policies and security measures.
Compatibility and Applicability
While this guide primarily uses Active Directory as an example, the configuration steps provided are applicable to a variety of LDAP servers including Red Hat Directory, Tivoli Directory, eDirectory and also OpenLDAP, 389 Directory Server, ApacheDS, and others. The principles of connecting and configuring LDAP remain consistent across different types of LDAP directory servers.
Additionally, ARTESCA identity management system can synchronize up to 10 000 users from an LDAP server integration.
Set up Authentication
To set up AD/LDAP authentication, follow this procedure:


