

Import Externally Signed Certificates
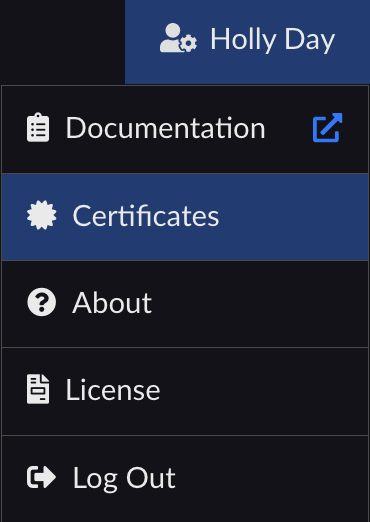
Click the username in the top right-hand corner and select Certificates on the drop-down list.
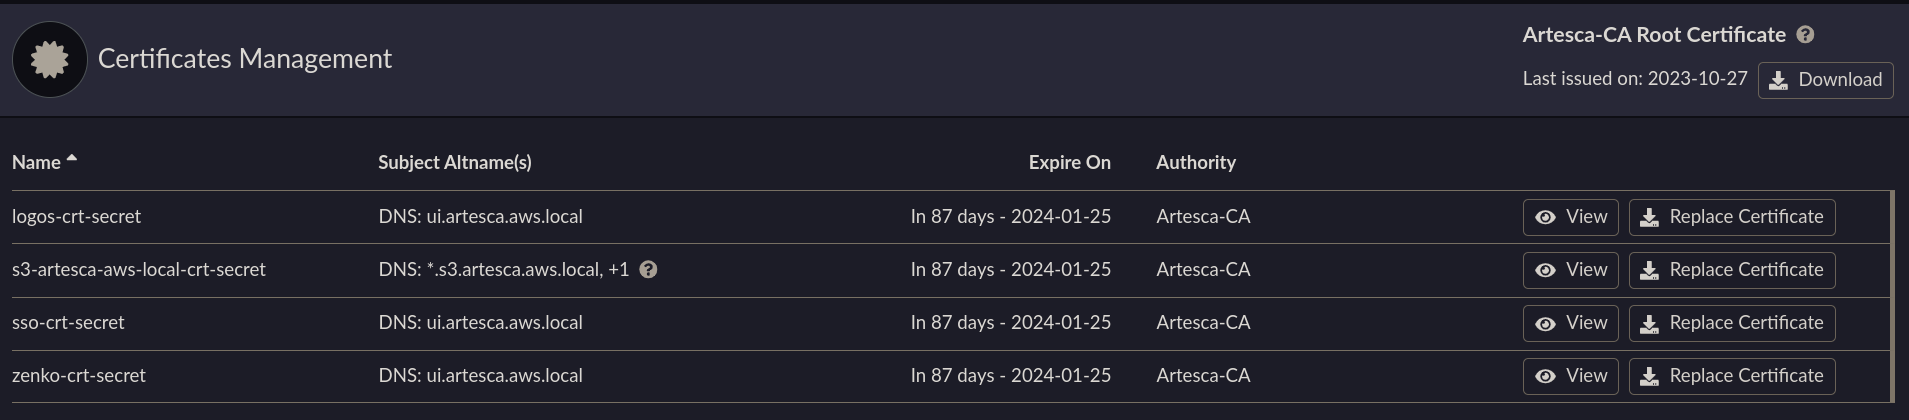
The list of certificates displays.
Note
The certificate management for the ARTESCA+ Veeam Unified Software Appliance differs from the regular ARTESCA one. It also depends on the architecture model.
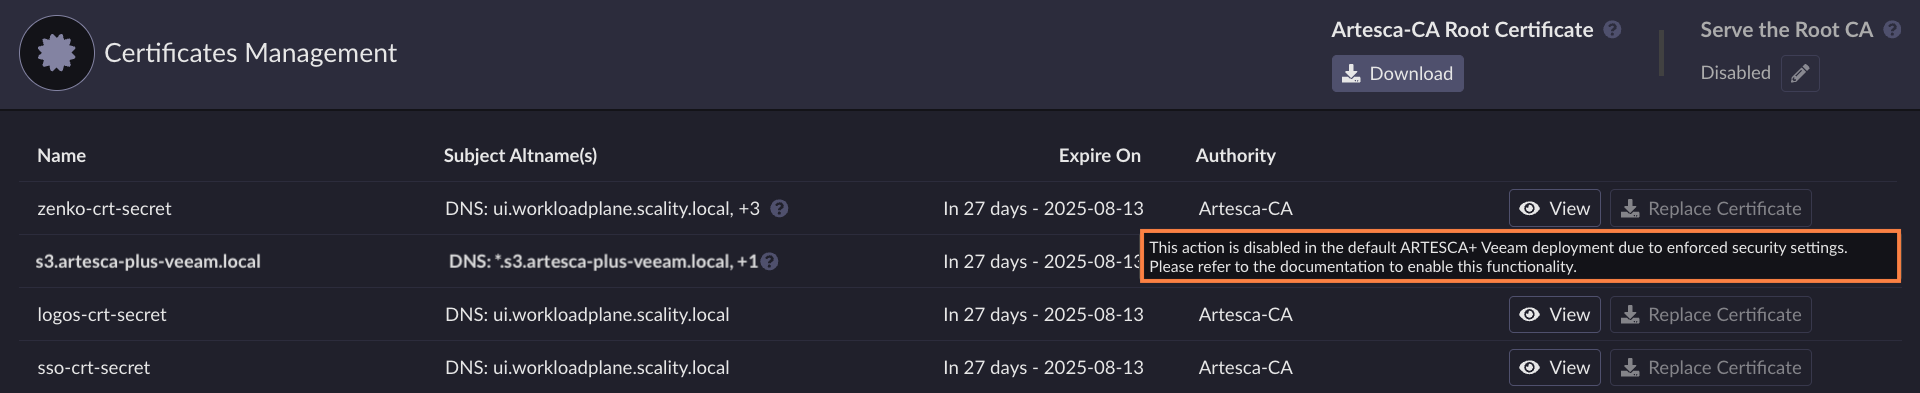
Primary Repository Architecture
To enforce the security of the primary repository architecture, the certificate management is disabled.
Secondary Repository Architecture
On a secondary repository architecture, only the ARTESCA+ Veeam S3 endpoint certificate management is disabled.
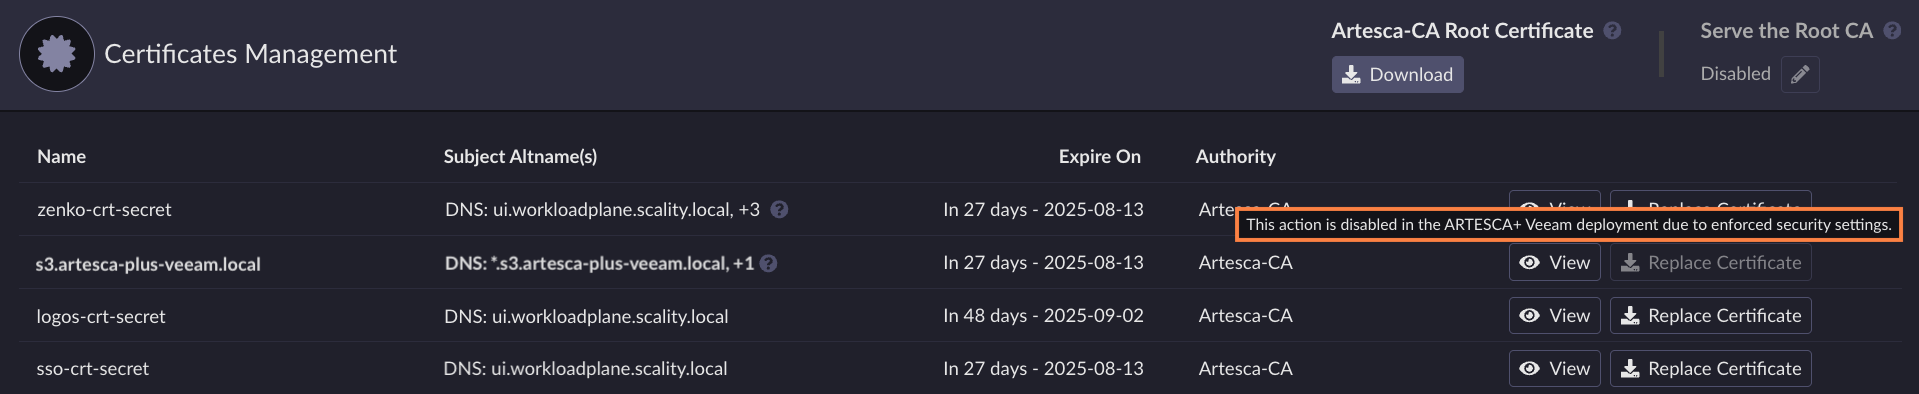
Click Replace Certificate next to the certificate you want to replace.
Tip
Click View to access the certificate’s details. Refer to View a Signed Certificate for more information.
(Optional) Edit the CSR with Organization specific information.
This optional step allows you to enrich the CSR with your Organization’s specific information and your Common Name to comply with your certificate management authority.
Check the Edit CSR with Organization specific information box. It expands to display a form with optional fields to fill in.
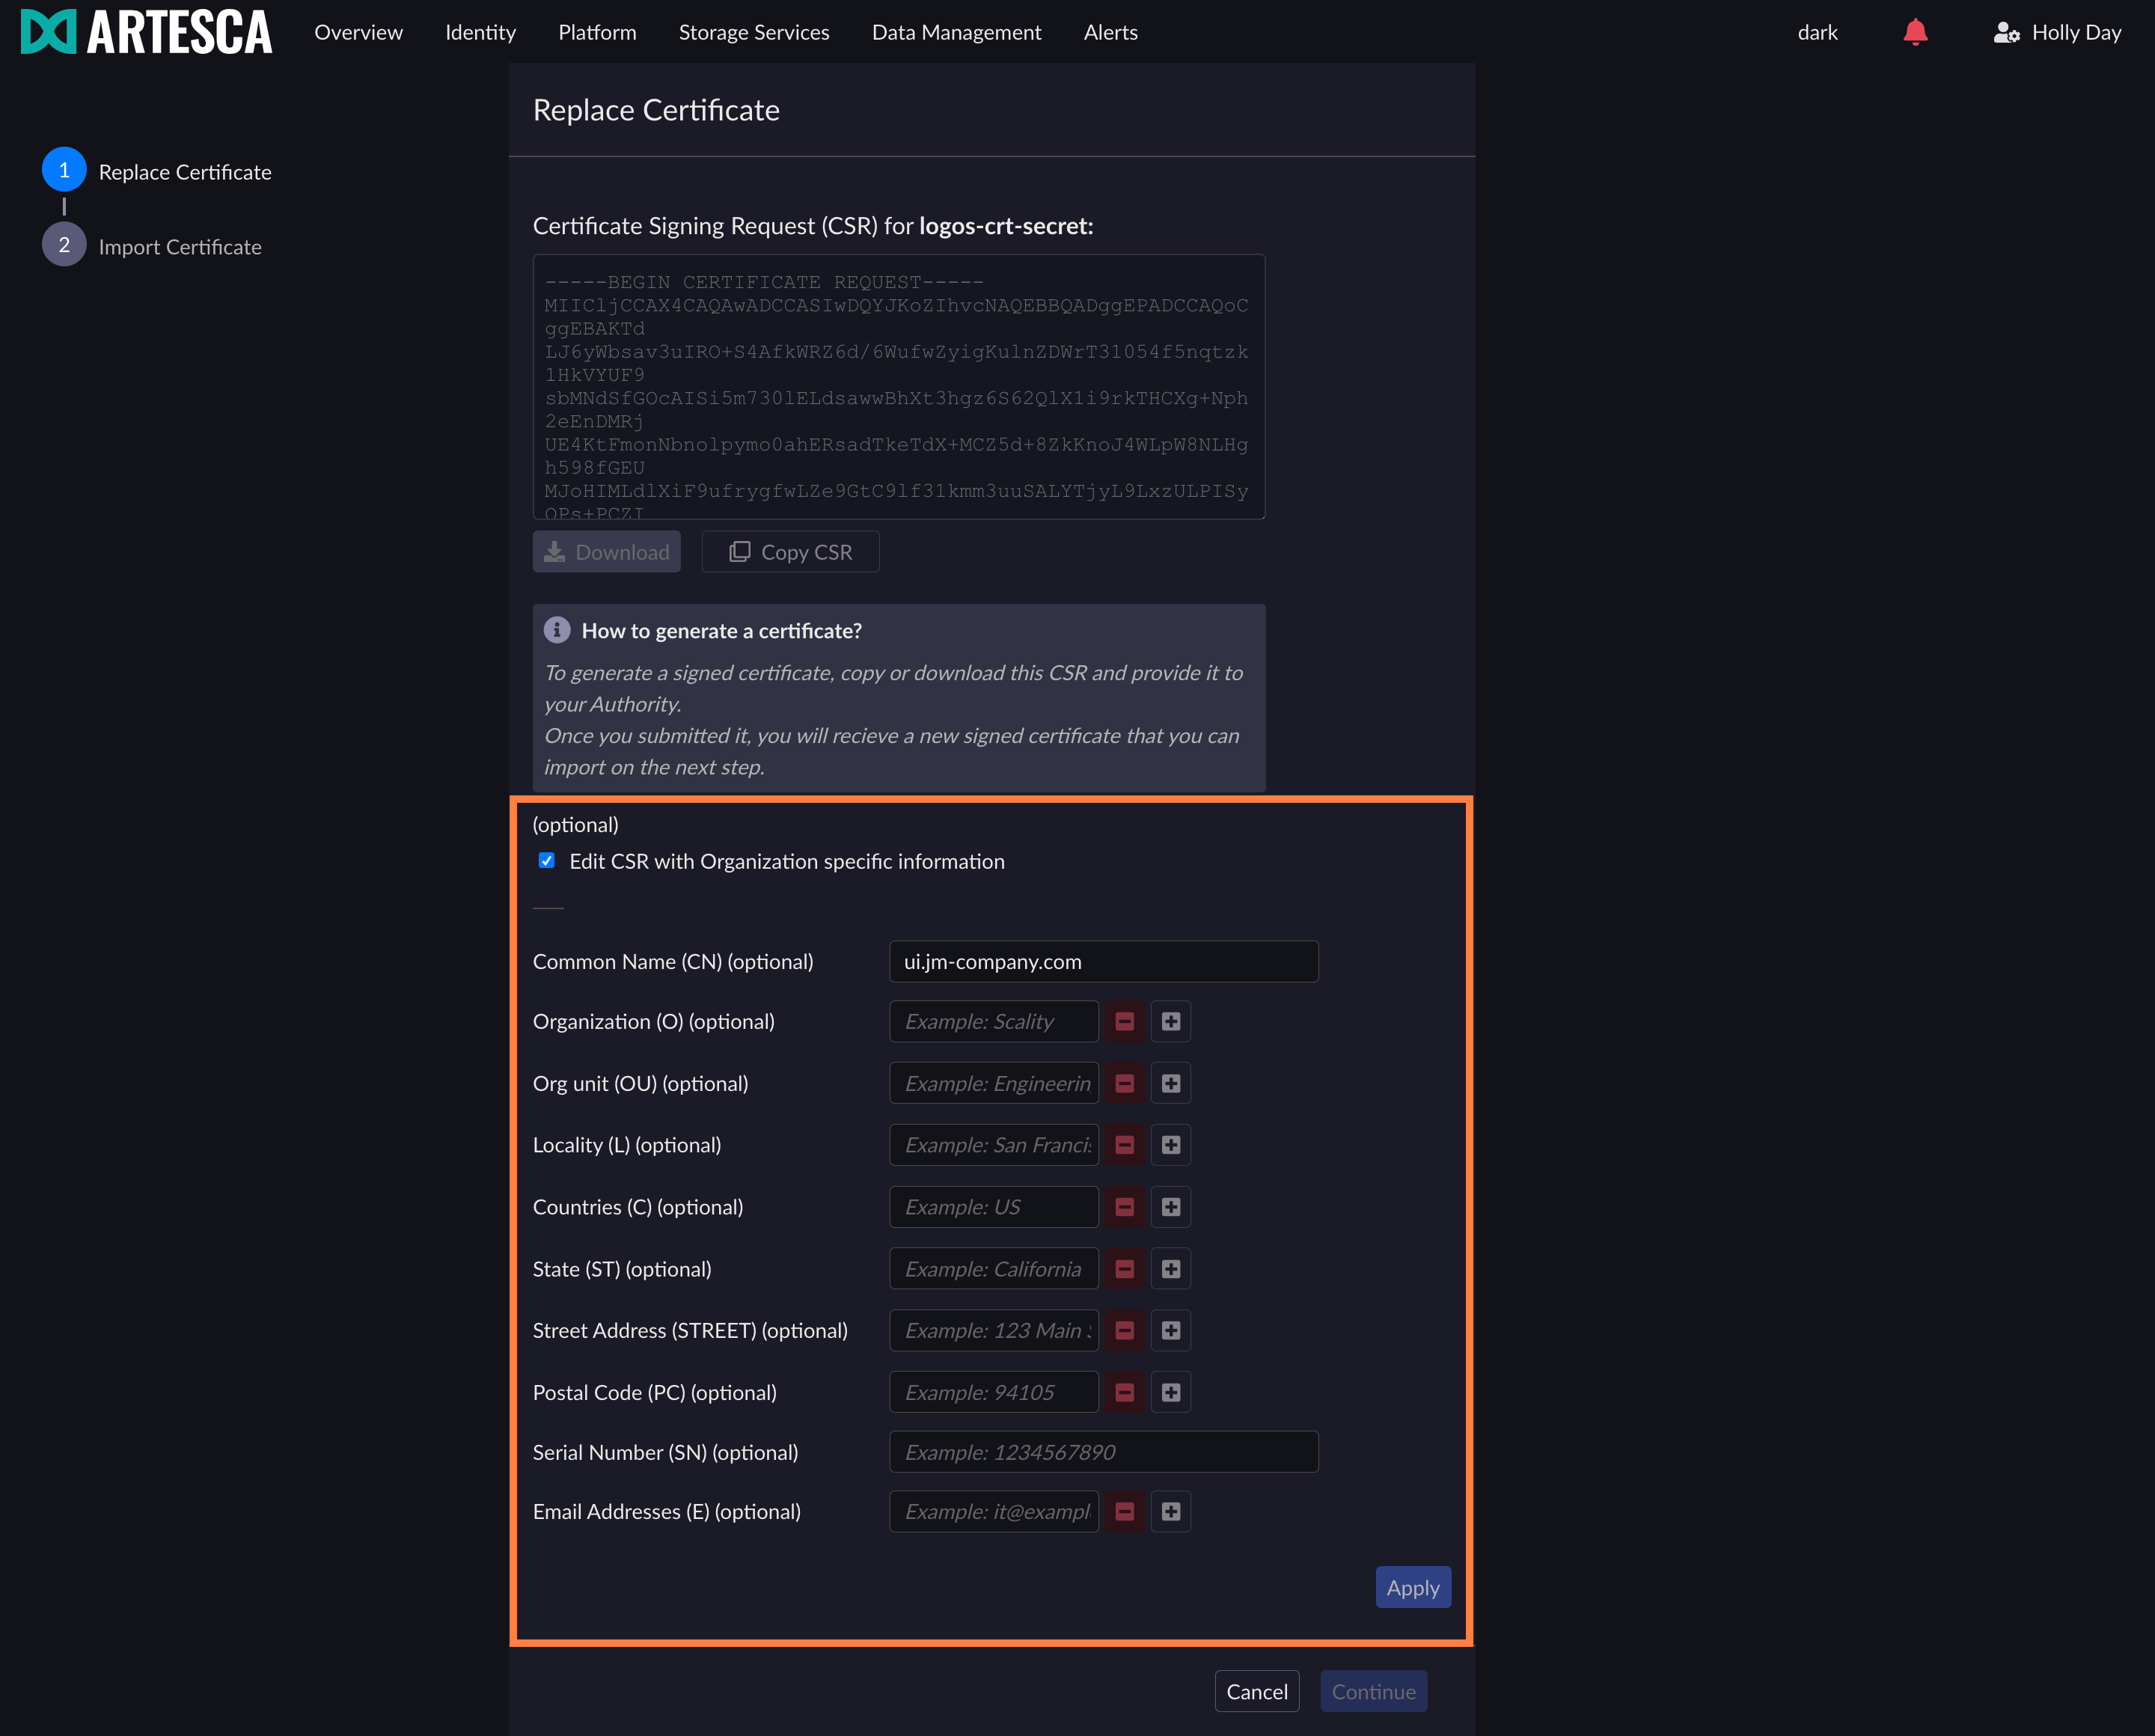
Fill in the form with your Organization’s specific information.
Click Apply to save your information and enrich your CSR.
Copy or download the Certificate Signing Request (CSR).

Submit the CSR to your Certificate Authority. You must receive a new certificate.
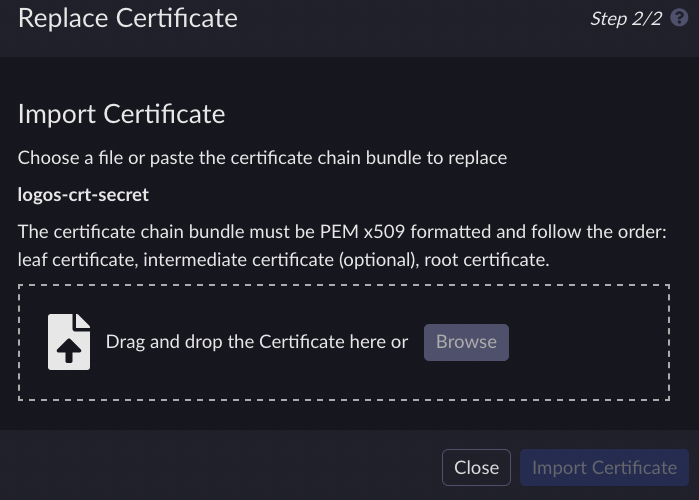
Import the certificate you received on the previous step, either by dragging or dropping the file.
Important
Make sure to include all certificates from the trust chain in the resulting bundle, and in the following order:
Leaf certificate
Intermediate certificate(s) (optional)
Root certificate
To use externally signed certificates (instead of letting ARTESCA manage them), follow these steps for each existing certificate:
Retrieve a Certificate Signing Request (CSR) corresponding to the considered certificate.
Use your CA to sign it.
Replace the generated certificate with your own in the existing Secret.
Here are the detailed steps, applied to each certificate:
Certificate zenko/zenko-crt-secret
Retrieve the current revision of the Certificate:
[artesca-os@bootstrap ~]$REVISION=$( sudo kubectl --kubeconfig /etc/kubernetes/admin.conf \ get --namespace zenko \ certificate/zenko-crt-secret -o jsonpath='{.status.revision}' )
Retrieve the corresponding
zenko-crt-secretCSR:[artesca-os@bootstrap ~]$TEMPLATE=" {{range .items}} {{if (and (eq (index .metadata.annotations \"cert-manager.io/certificate-name\") \"zenko-crt-secret\" ) (eq (index .metadata.annotations \"cert-manager.io/certificate-revision\") \"$REVISION\" ) ) }} {{.spec.request}} {{end}} {{end}}" sudo kubectl --kubeconfig /etc/kubernetes/admin.conf \ get --namespace zenko certificaterequest \ --output go-template="${TEMPLATE//$'\n'}" | \ base64 -d > zenko-crt-secret.csr
Generate the certificate from the
zenko-crt-secretCSR.Important
When signing the CSR with your CA, make sure to copy the requested extensions over to the certificate. Otherwise, you will lose the required key usages and subject alternative names, needed for the certificate to function properly.
With OpenSSL version 3, you can use the -copy_extensions copy option.
Update the
zenko-crt-secretSecret with the new certificate:[artesca-os@bootstrap ~]$sudo kubectl --kubeconfig /etc/kubernetes/admin.conf \ patch --namespace zenko \ secret/zenko-crt-secret \ --patch ' data: tls.crt: '$(base64 -w0 ./zenko-crt-secret.crt)' ca.crt: '$(base64 -w0 ./CA.crt)' '
Note
Replace
./zenko-crt-secret.crtwith the path to your new certificate. And./CA.crtwith the path to your CA certificate.
Certificate artesca-auth/sso-crt-secret
Retrieve the current revision of the Certificate:
[artesca-os@bootstrap ~]$REVISION=$( sudo kubectl --kubeconfig /etc/kubernetes/admin.conf \ get --namespace artesca-auth \ certificate/sso-crt-secret -o jsonpath='{.status.revision}' )
Retrieve the corresponding
sso-crt-secretCSR:[artesca-os@bootstrap ~]$TEMPLATE=" {{range .items}} {{if (and (eq (index .metadata.annotations \"cert-manager.io/certificate-name\") \"sso-crt-secret\" ) (eq (index .metadata.annotations \"cert-manager.io/certificate-revision\") \"$REVISION\" ) ) }} {{.spec.request}} {{end}} {{end}}" sudo kubectl --kubeconfig /etc/kubernetes/admin.conf \ get --namespace artesca-auth certificaterequest \ --output go-template="${TEMPLATE//$'\n'}" | \ base64 -d > sso-crt-secret.csr
Generate the certificate from the
sso-crt-secretCSR.Important
When signing the CSR with your CA, make sure to copy the requested extensions over to the certificate. Otherwise, you will lose the required key usages and subject alternative names, needed for the certificate to function properly.
With OpenSSL version 3, you can use the -copy_extensions copy option.
Update the
sso-crt-secretSecret with the new certificate:[artesca-os@bootstrap ~]$sudo kubectl --kubeconfig /etc/kubernetes/admin.conf \ patch --namespace artesca-auth \ secret/sso-crt-secret \ --patch ' data: tls.crt: '$(base64 -w0 ./sso-crt-secret.crt)' ca.crt: '$(base64 -w0 ./CA.crt)' '
Note
Replace
./sso-crt-secret.crtwith the path to your new certificate. And./CA.crtwith the path to your CA certificate.
Special case: Import Externally Signed Certificates for S3 Endpoints
There are two cases to consider (repeat the steps for each endpoint):
In this scenario, follow these steps:
Generate a certificate with the following mandatory x509 v3 extensions (the choice of Subject is not important for the functioning of ARTESCA, refer to your security team for recommendations):
Subject Alternative Names: must include
DNS:<your S3 endpoint>andDNS:*.<your S3 endpoint>(this wildcard domain is used for virtual-host style S3 access)Key Usages: must include
digitalSignatureandkeyEnciphermentExtended Key Usages: must include
serverAuth
Copy the generated certificate and private key to your bootstrap node. They will be named
s3.keyands3.crtrespectively in the following steps.Define a Secret name (make sure it is not already in use):
[artesca-os@bootstrap ~]$SECRET_NAME="s3-cert"
Create a TLS Secret containing the key and certificates:
[artesca-os@bootstrap ~]$sudo kubectl --kubeconfig /etc/kubernetes/admin.conf \ -n zenko create secret tls $SECRET_NAME \ --key="s3.key" --cert="s3.crt"
Define your endpoint in a variable:
[artesca-os@bootstrap ~]$S3_ENDPOINT="s3.my-company.com"
Add an entry for your endpoint in the
Zenkodeployment:[artesca-os@bootstrap ~]$sudo kubectl --kubeconfig /etc/kubernetes/admin.conf patch \ --namespace zenko zenko/artesca-data \ --type json --patch ' [{ "op": "add", "path": "/spec/ingress/certificates/-", "value": { "hosts": ["'$S3_ENDPOINT'", "'*.$S3_ENDPOINT'"], "secretName": "'$SECRET_NAME'" } }] '
In this scenario, you have to follow the same procedure as above for the three certificates:
zenko/zenko-crt-secret
For S3 endpoints, there are two cases to consider (repeat the steps for each endpoint):
The certificate was already generated by using one of the above methods (built-in or custom CA).
In this scenario, assuming the chosen Secret name was
s3-cert, follow these steps:Certificate
zenko/s3-certRetrieve the current revision of the Certificate:
[artesca-os@bootstrap ~]$REVISION=$( sudo kubectl --kubeconfig /etc/kubernetes/admin.conf \ get --namespace zenko \ certificate/s3-cert -o jsonpath='{.status.revision}' )
Retrieve the corresponding
s3-certCSR:[artesca-os@bootstrap ~]$TEMPLATE=" {{range .items}} {{if (and (eq (index .metadata.annotations \"cert-manager.io/certificate-name\") \"s3-cert\" ) (eq (index .metadata.annotations \"cert-manager.io/certificate-revision\") \"$REVISION\" ) ) }} {{.spec.request}} {{end}} {{end}}" sudo kubectl --kubeconfig /etc/kubernetes/admin.conf \ get --namespace zenko certificaterequest \ --output go-template="${TEMPLATE//$'\n'}" | \ base64 -d > s3-cert.csr
Generate the certificate from the
s3-certCSR.Important
When signing the CSR with your CA, make sure to copy the requested extensions over to the certificate. Otherwise, you will lose the required key usages and subject alternative names, needed for the certificate to function properly.
With OpenSSL version 3, you can use the -copy_extensions copy option.
Update the
s3-certSecret with the new certificate:[artesca-os@bootstrap ~]$sudo kubectl --kubeconfig /etc/kubernetes/admin.conf \ patch --namespace zenko \ secret/s3-cert \ --patch ' data: tls.crt: '$(base64 -w0 ./s3-cert.crt)' ca.crt: '$(base64 -w0 ./CA.crt)' '
Note
Replace
./s3-cert.crtwith the path to your new certificate. And./CA.crtwith the path to your CA certificate.
The certificate has not been generated yet.
In this scenario, follow these steps:
Generate a certificate with the following mandatory x509 v3 extensions (the choice of Subject is not important for the functioning of ARTESCA, refer to your security team for recommendations):
Subject Alternative Names: must include
DNS:<your S3 endpoint>andDNS:*.<your S3 endpoint>(this wildcard domain is used for virtual-host style S3 access)Key Usages: must include
digitalSignatureandkeyEnciphermentExtended Key Usages: must include
serverAuth
Copy the generated certificate and private key to your bootstrap node. They will be named
s3.keyands3.crtrespectively in the following steps.Define a Secret name (make sure it is not already in use):
[artesca-os@bootstrap ~]$SECRET_NAME="s3-cert"
Create a TLS Secret containing the key and certificates:
[artesca-os@bootstrap ~]$sudo kubectl --kubeconfig /etc/kubernetes/admin.conf \ -n zenko create secret tls $SECRET_NAME \ --key="s3.key" --cert="s3.crt"
Define your endpoint in a variable:
[artesca-os@bootstrap ~]$S3_ENDPOINT="s3.my-company.com"
Add an entry for your endpoint in the
Zenkodeployment:[artesca-os@bootstrap ~]$sudo kubectl --kubeconfig /etc/kubernetes/admin.conf patch \ --namespace zenko zenko/artesca-data \ --type json --patch ' [{ "op": "add", "path": "/spec/ingress/certificates/-", "value": { "hosts": ["'$S3_ENDPOINT'", "'*.$S3_ENDPOINT'"], "secretName": "'$SECRET_NAME'" } }] '


