

Force Renew ARTESCA Built-In Certificate
Important
The procedure to force the renewal of built-in certificates does not apply to the ARTESCA+ Veeam Unified Software Appliance.
When using the ARTESCA built-in certificate method, the certificate will be automatically renewed every 90 days, and the renewal will happen one hour before certificate expiration. The following procedure explains how to force the renewal of the certificate before it expires.
Important
This procedure is only applicable when using ARTESCA built-in Certificate Authority.
Log in to the UI and click the username on the right side of the main menu. In this example the username is Sample User.
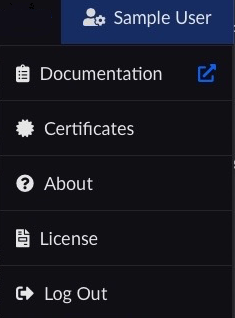
Select Certificates to view the Certificate Management page.

Take note of the certificate name that you want to renew.
Run the following script from one of the nodes in your cluster. In this example, the certificate name is
sso-crt-secret.[artesca-os@bootstrap ~]$CERTIFICATE_NAME_AS_SEEN_IN_UI=sso-crt-secret SECRET_NAME=$(sudo kubectl --kubeconfig=/etc/kubernetes/admin.conf get certificate -A --field-selector=metadata.name=$CERTIFICATE_NAME_AS_SEEN_IN_UI -o jsonpath={.items[0].spec.secretName}) NAMESPACE=$(sudo kubectl --kubeconfig=/etc/kubernetes/admin.conf get certificate -A --field-selector=metadata.name=$CERTIFICATE_NAME_AS_SEEN_IN_UI -o jsonpath={.items[0].metadata.namespace}) sudo kubectl --kubeconfig=/etc/kubernetes/admin.conf delete secret $SECRET_NAME -n $NAMESPACE
This command triggers the certificate renewal. The new certificate is valid for three months, and will be renewed 1 hour before its expiration date.


